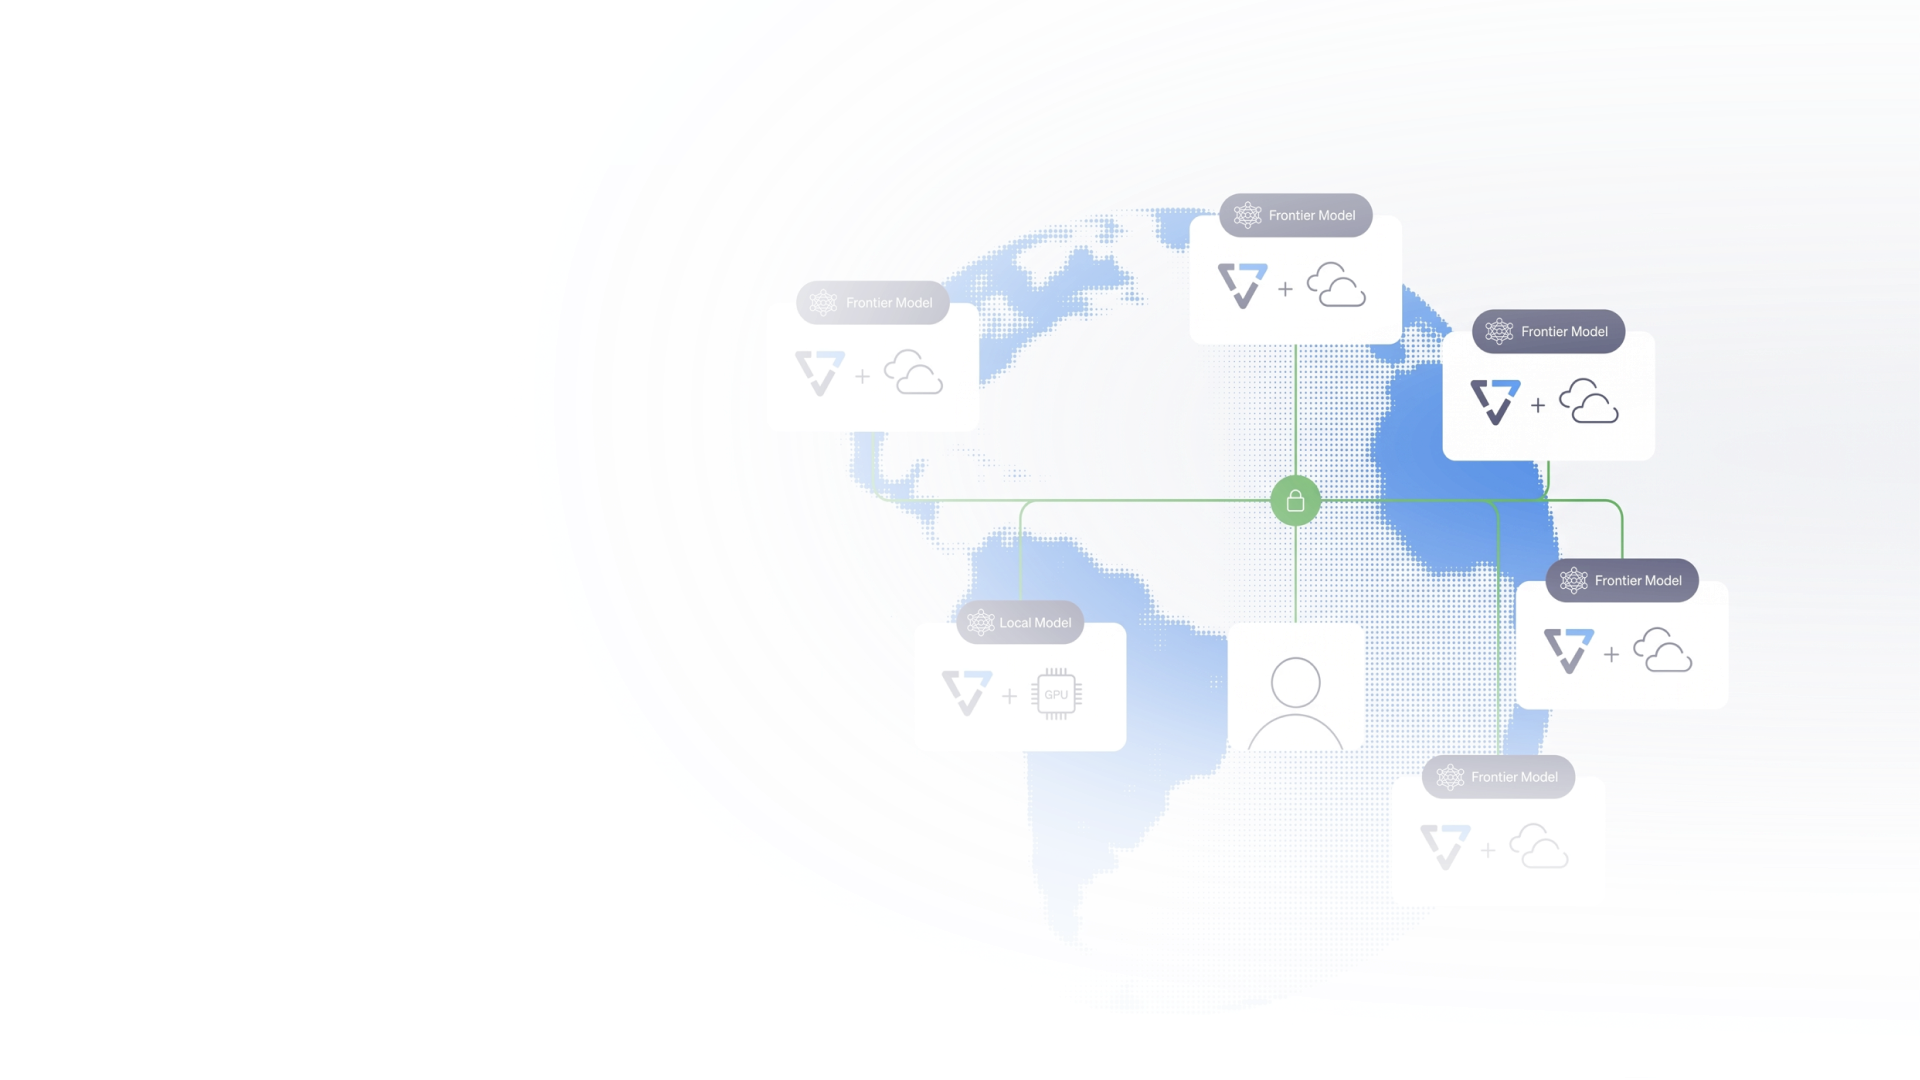
Bring Frontier AI to Your Most Sensitive Data
Run proprietary and fine-tuned AI models on regulated and sensitive enterprise data while protecting both data and model IP throughout processing with hardware-isolated confidential execution.
Bringing Advanced AI to Sensitive Data Requires a New Trust Model
Organizations want to apply state-of-the-art AI to their most valuable data, but traditional deployment models create a fundamental trust problem. Sensitive data cannot leave controlled environments, while proprietary models cannot be exposed inside infrastructure their owners do not trust.
Sensitive Data Must Remain Under Enterprise Control
Regulatory, sovereignty, and security requirements can prevent sensitive enterprise data from moving to externally hosted AI services or beyond established security boundaries.
Proprietary Model IP Can’t Be Exposed
Model weights represent valuable intellectual property. Model providers need to serve enterprise customers without exposing proprietary assets to customers, infrastructure operators, or administrators.
Active AI Workloads Remain Exposed
Protecting data at rest and in transit is not enough. During AI processing, privileged infrastructure operators may otherwise have access to sensitive data, model weights, or workload memory.
Protect AI Beyond Data at Rest and in Transit
Enterprise security has long focused on protecting data at rest and in transit. AI introduces a third requirement: protecting data and models while they are actively being processed across CPUs and GPUs.
This matters because the most valuable AI workloads increasingly bring together assets owned by different parties. Enterprises need to retain control of sensitive and regulated data. Model providers need to protect proprietary model weights. Neither should have to trust the infrastructure operator with those assets.
Confidential computing changes that trust model. Hardware-isolated execution and cryptographic attestation create verified environments where protected assets become accessible only after the environment proves that it meets approved security requirements. Enterprises can bring frontier AI to sensitive data while data owners and model providers retain independent control of their assets.
Establish Trust Before Access Is Granted
VAST enables confidential AI through VAST DataEnclave, the confidential AI capability of VAST DataEngine. Hardware-isolated execution, cryptographic attestation, independent key control, and auditability enable sensitive data and proprietary models to operate together without exposing either to the underlying infrastructure.
Protect Data in Action
Extend protection beyond data at rest and in transit to sensitive data and proprietary models while AI workloads are actively processing them.
Verify Before Decrypt
Cryptographically attest the hardware, software environment, and workload configuration against approved security policies before access to protected assets is granted.
Keep Both Sides in Control
Allow enterprise data and proprietary model IP to remain protected under their respective owners' keys, without transferring key ownership to the infrastructure operator.
Maintain Auditability
Capture attestation, key release, policy decisions, and workload activity in a tamper-proof, queryable audit trail without exposing protected assets.
Protect Data and Models Throughout AI Execution
Protect AI with Hardware-Isolated Execution
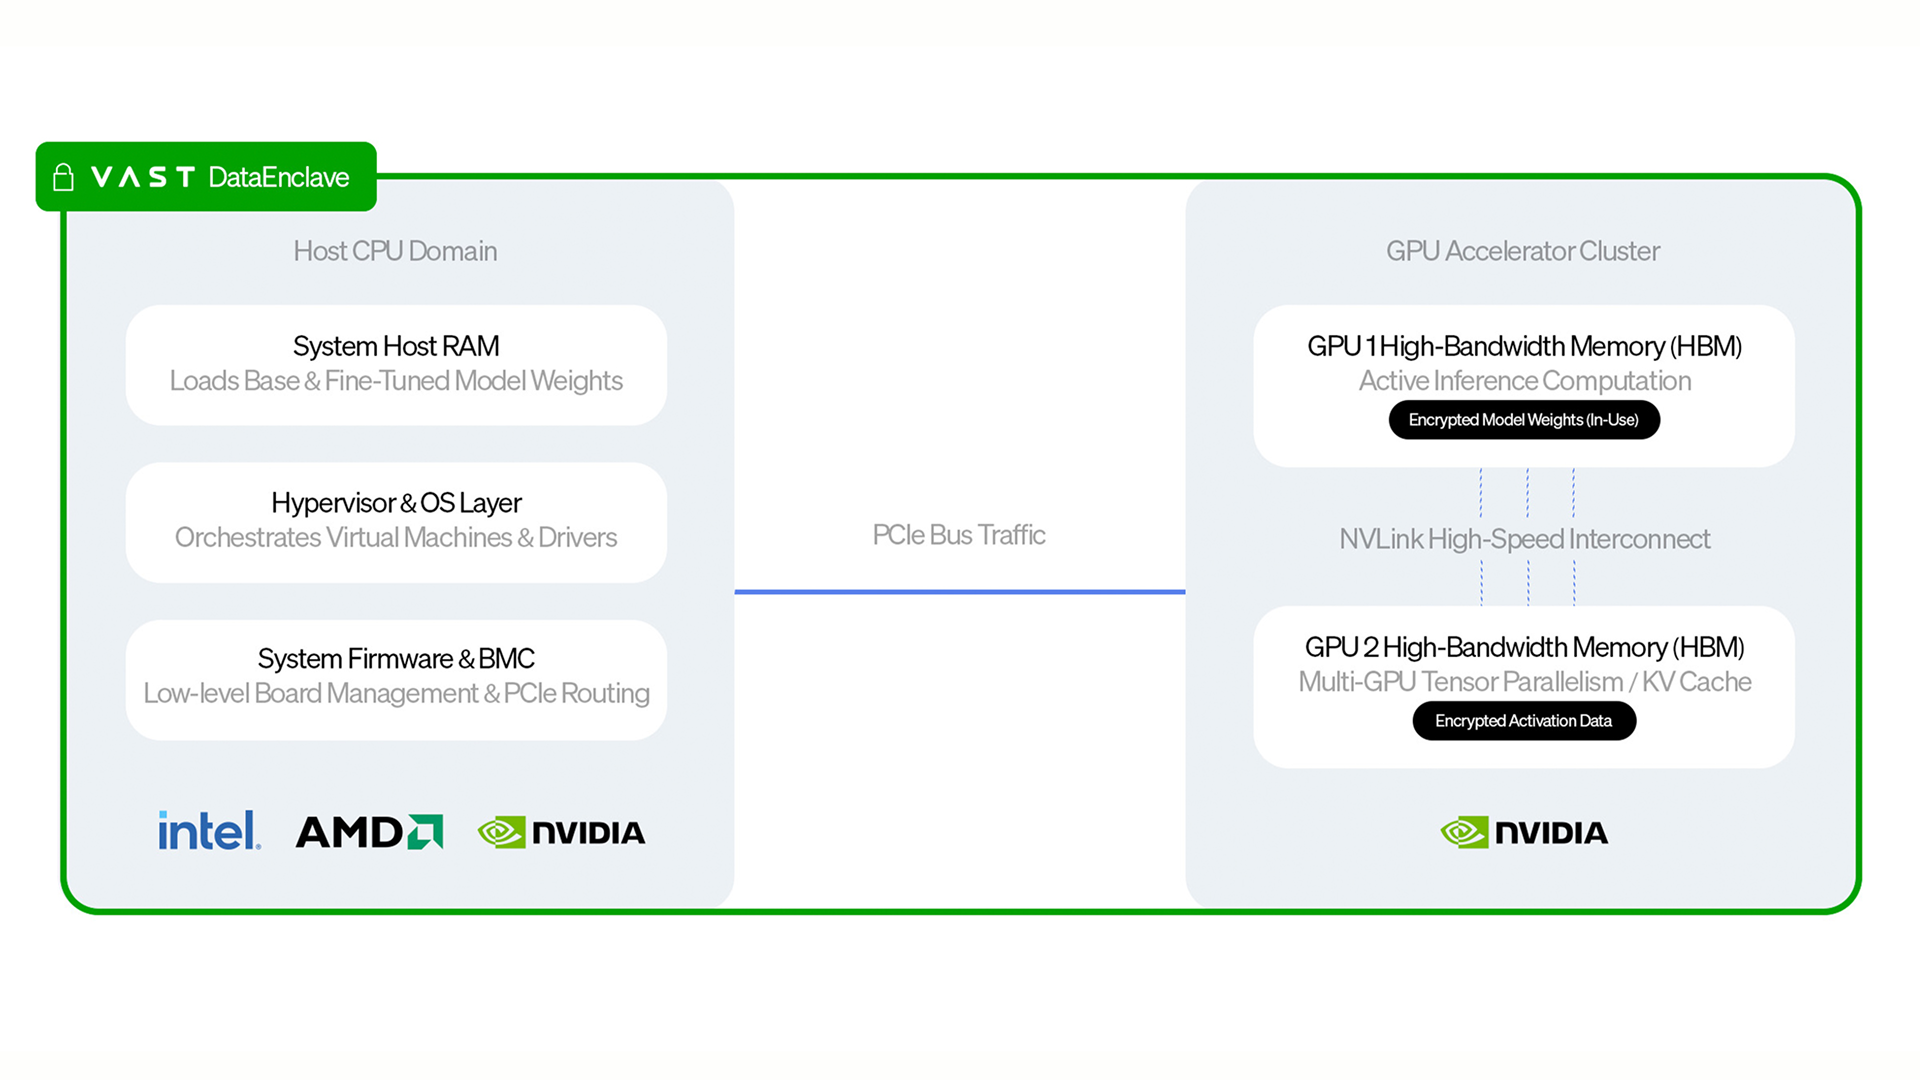
Traditional infrastructure can leave sensitive data and model weights exposed while AI is running. Confidential AI runs workloads inside hardware-isolated environments spanning CPU and accelerated GPU execution, protecting sensitive data and models from the underlying infrastructure while preserving familiar AI frameworks and deployment models.
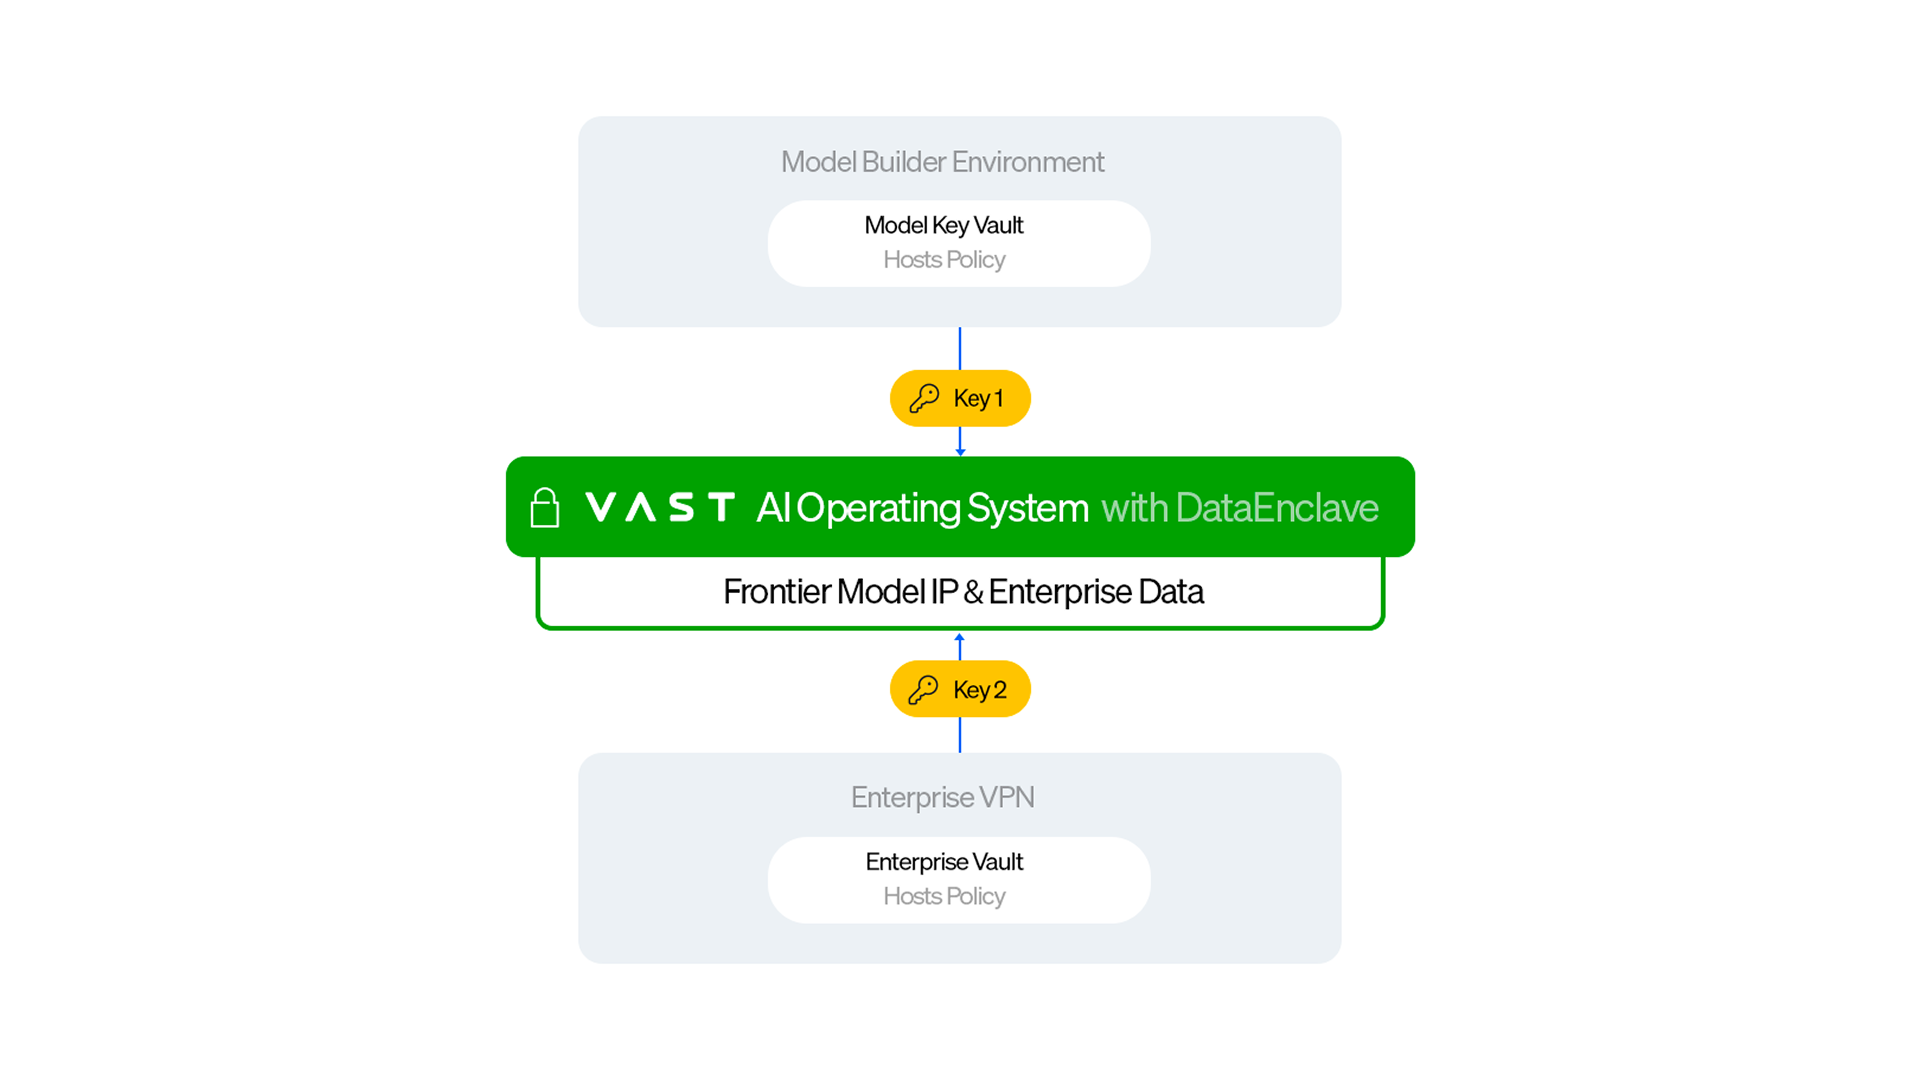
Verify the Environment Before Releasing Keys
Hardware isolation alone does not establish trust. Cryptographic attestation verifies the environment against approved security policies before keys and secrets are released. If the environment fails verification, they remain unavailable, creating a verify-before-decrypt trust model.
Preserve Independent Control of Data and Models
Confidential AI creates a neutral execution environment where enterprises and model providers can work together without surrendering control of protected assets. Enterprise data and proprietary model weights remain under their respective owners' key control and become accessible only inside an approved confidential environment.
Maintain Visibility Without Exposing Protected Assets
Confidential workloads still require operational and compliance visibility. VAST maintains a tamper-proof, queryable record of attestation, key releases, policy decisions, and workload lifecycle activity, allowing teams to verify what ran and under what policy without exposing protected data or models.
Why VAST DataEnclave?
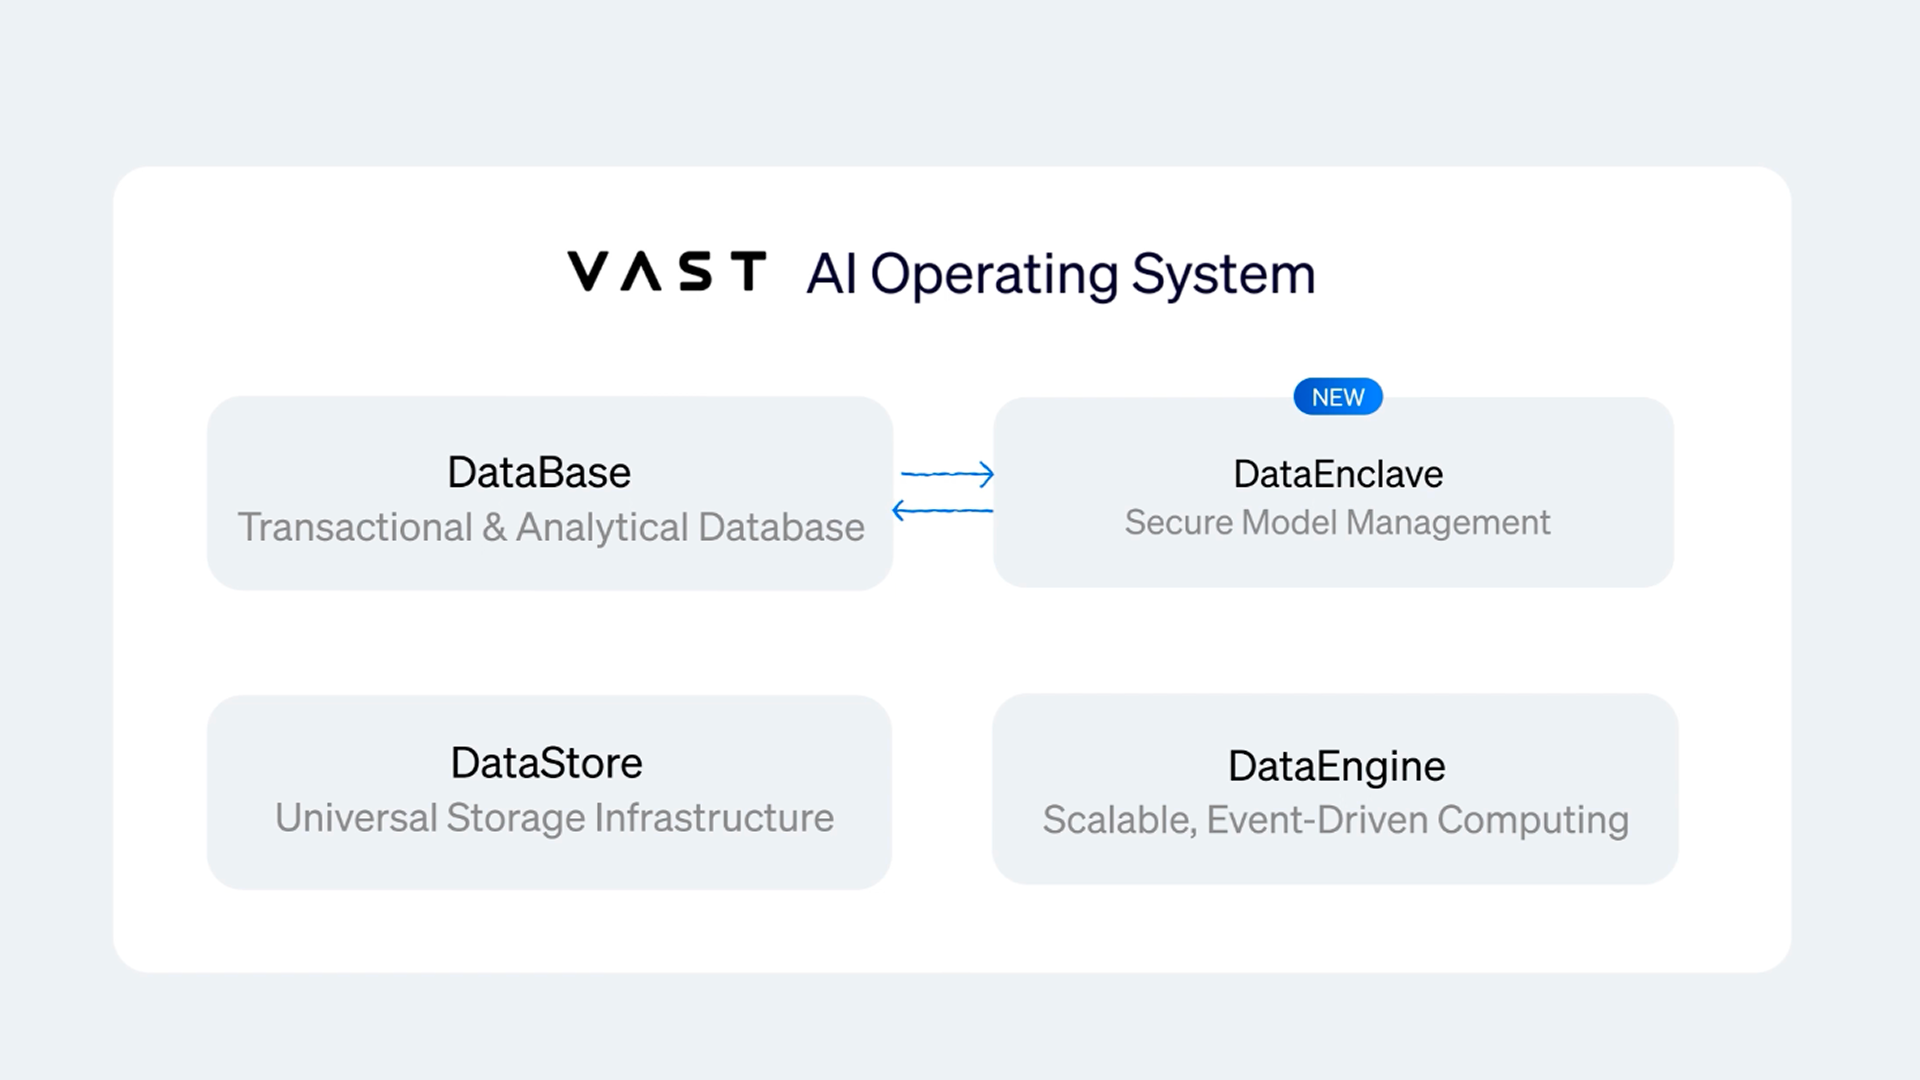
VAST DataEnclave brings confidential AI directly into the VAST AI Operating System, combining secure container execution and cryptographic attestation with customer-controlled and third-party key management. As a capability of VAST DataEngine, DataEnclave extends VAST's data protection model from data at rest and in flight to data and models in action.
Confidential CPU + GPU Execution
Run AI workloads in hardware-isolated environments that protect sensitive data and proprietary models across CPU and accelerated GPU execution.
Attestation & Verification
Generate and verify cryptographic evidence that the hardware, software environment, and workload configuration satisfy approved policies before access to protected assets is granted.
Independent Key Control
Integrate with enterprise and model-provider key management infrastructure so data owners retain control of the cryptographic keys protecting their respective assets.
Connected or Air-Gapped
Deploy confidential AI across connected, private, sovereign, and fully air-gapped environments while maintaining the same verify-before-decrypt trust model.
Operationalize Confidential AI Where Your Data Lives
VAST DataEngine provides the execution and orchestration layer for confidential AI. DataEnclave integrates secure container execution and attestation directly into DataEngine, allowing organizations to run protected AI workloads alongside event-driven pipelines, serverless functions, containers, and AI services on the same data platform.
Execute Where Data Lives
Run AI workloads where enterprise data resides, bringing compute, pipelines, and AI processing closer to the data while reducing unnecessary data movement.
Automate AI Pipelines
Use event-driven pipelines to initiate data processing, enrichment, vectorization, inference, and downstream AI workflows as new data arrives.
Deploy Familiar AI Workloads
Run containerized applications, AI services, and custom workloads using familiar development and deployment models on the same platform as your data and AI pipelines.
Govern and Observe Execution
Track workload activity and execution across AI pipelines while DataEnclave provides auditable records of attestation, policy decisions, and key release for confidential workloads.
Protect What Matters Across the AI Ecosystem
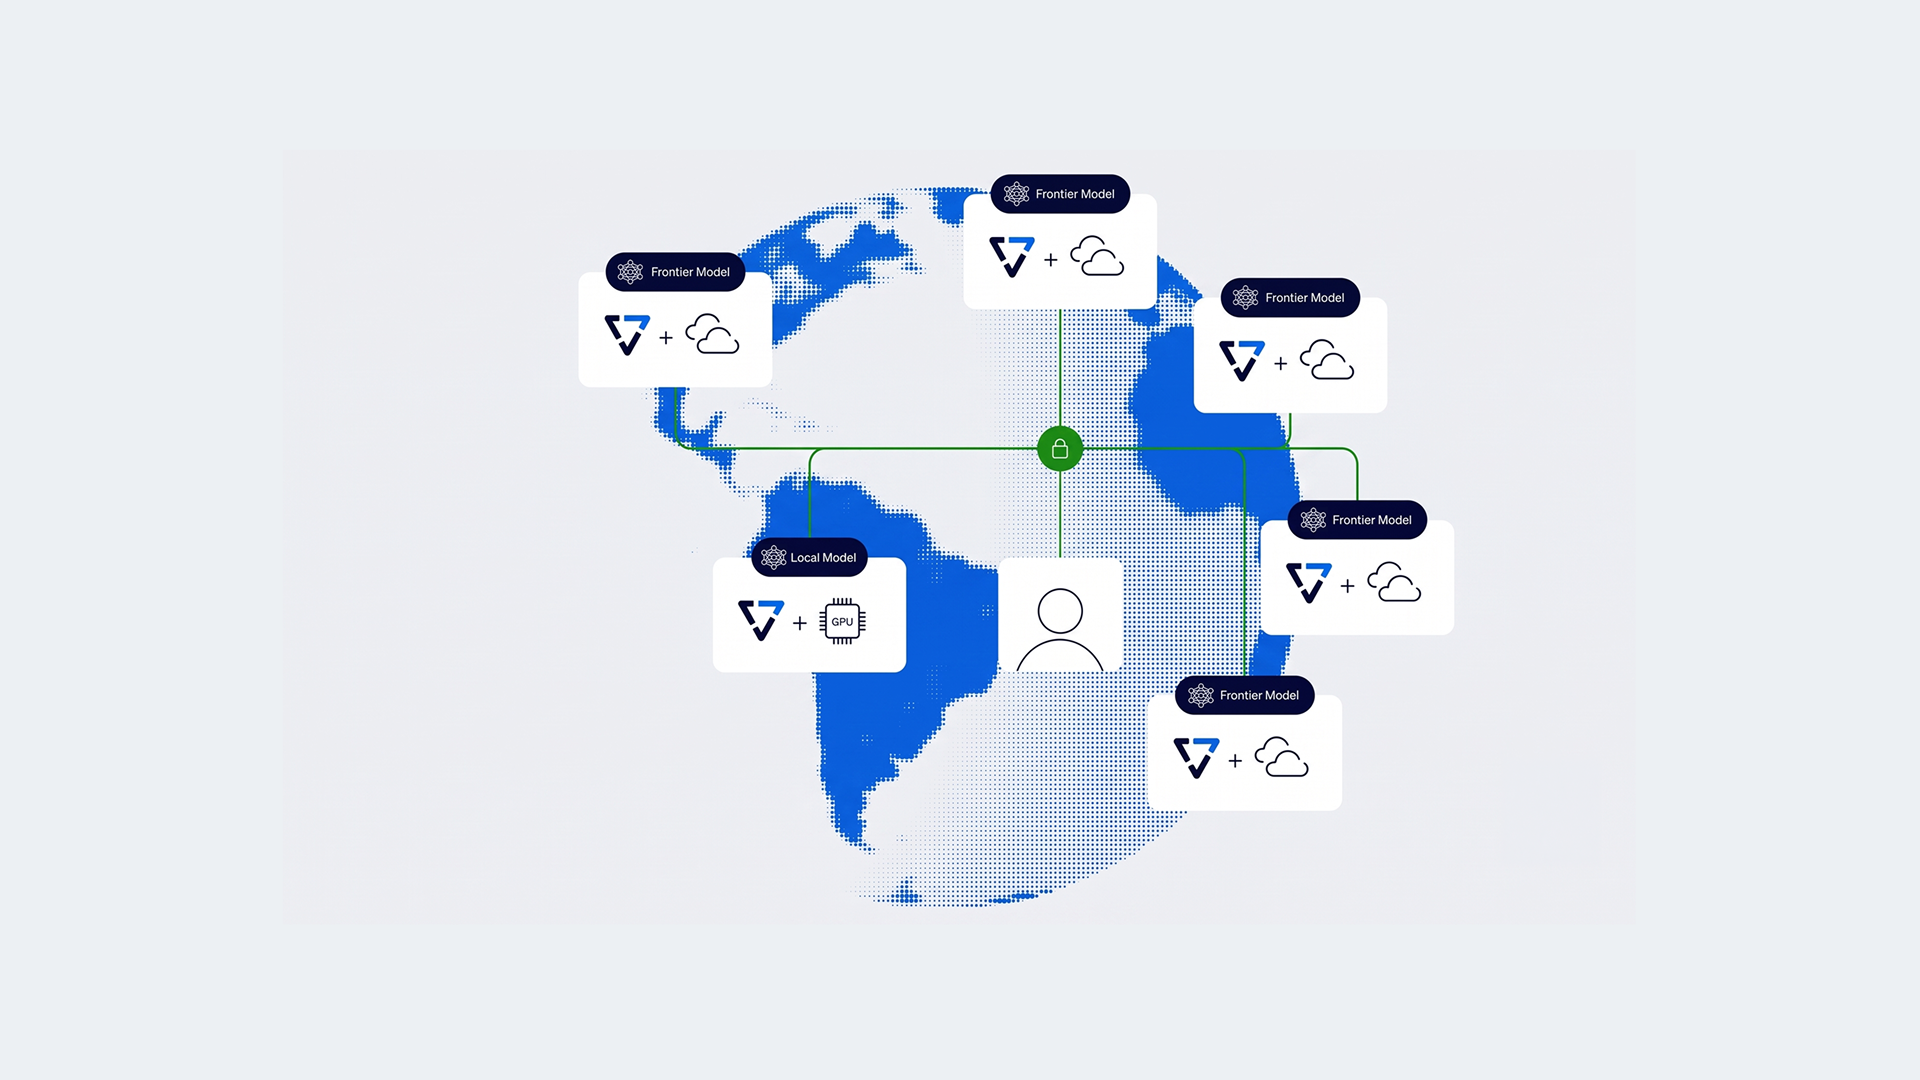
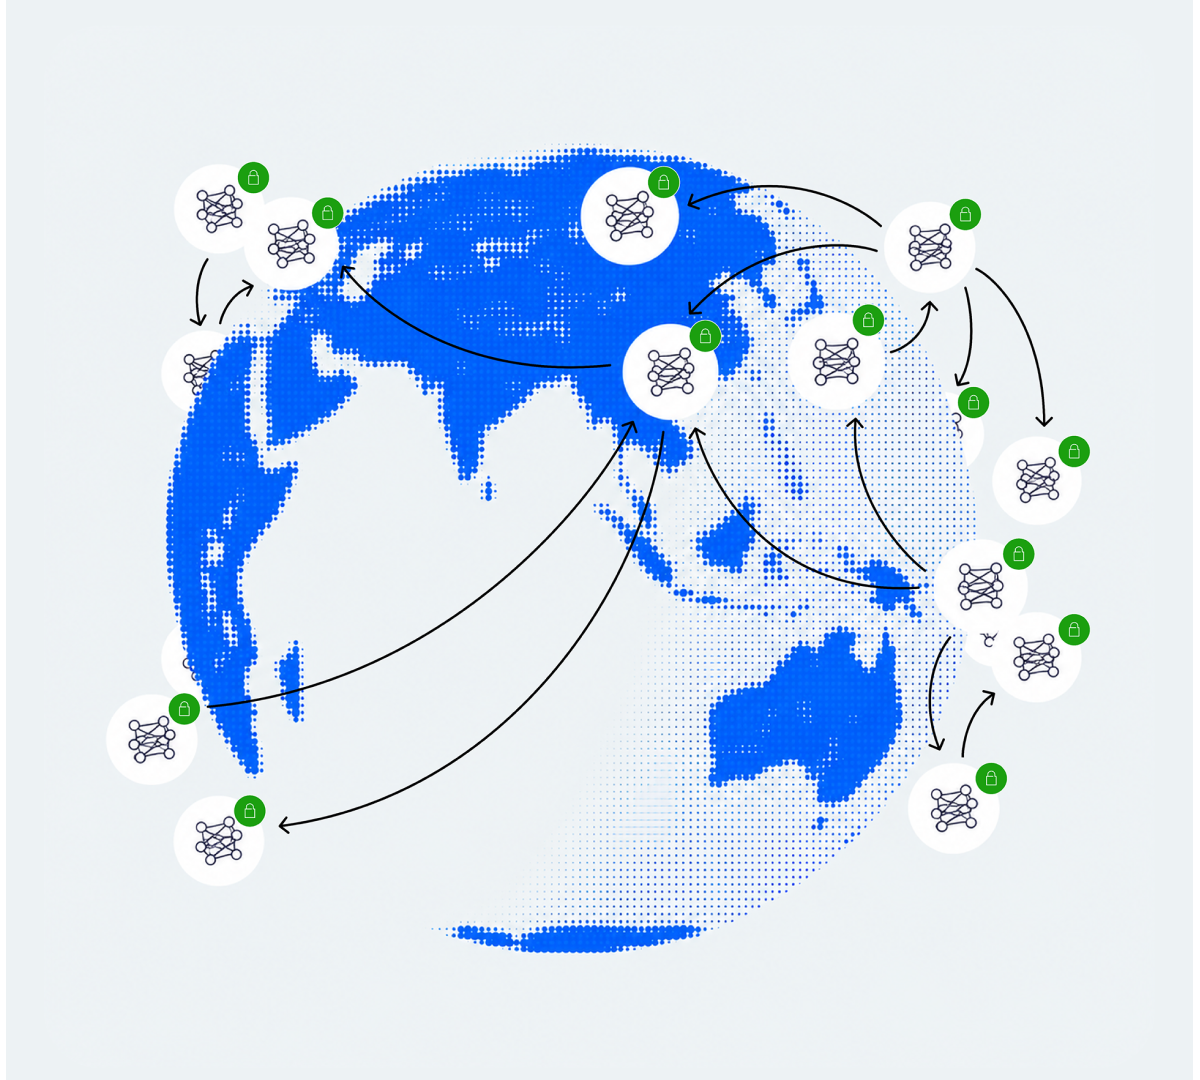
Confidential AI enables enterprises, model builders, AI cloud providers, and infrastructure partners to work together without requiring any party to relinquish control of sensitive data, proprietary models, or critical infrastructure.
Enterprise: Advanced AI for Sensitive Data
Run proprietary foundation models and fine-tuned AI against regulated data inside your security domain, bringing advanced AI to sensitive workloads without surrendering control of enterprise data.
Model Builders: Reach Regulated Customers
Bring proprietary, closed-weight models to sensitive enterprise workloads while protecting model IP, enabling customers to use advanced models within their required security boundaries.
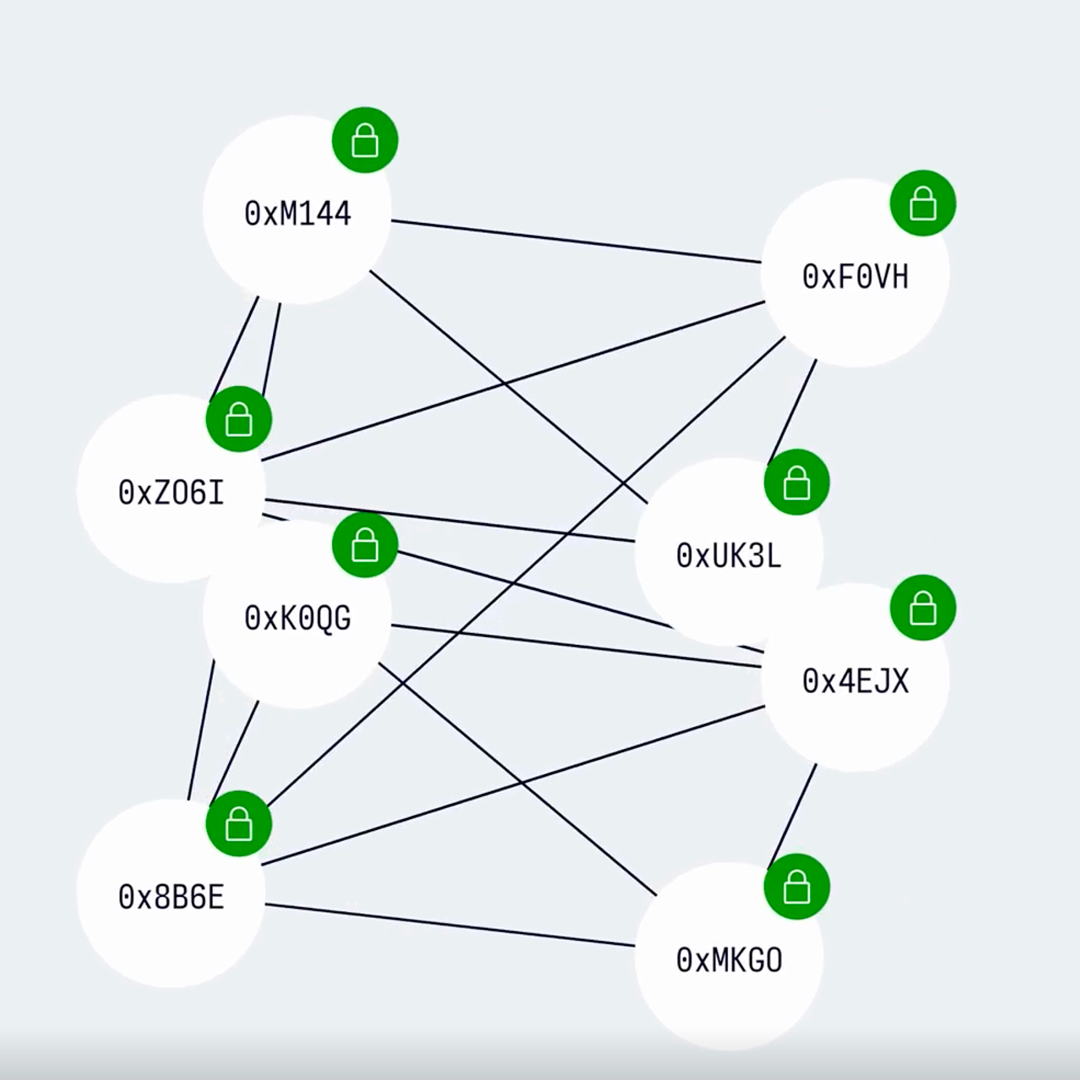
Cloud Providers: Host AI Without Access
Host proprietary models and regulated enterprise data without gaining access to either, enabling sensitive AI workloads while maintaining required security and sovereignty boundaries.
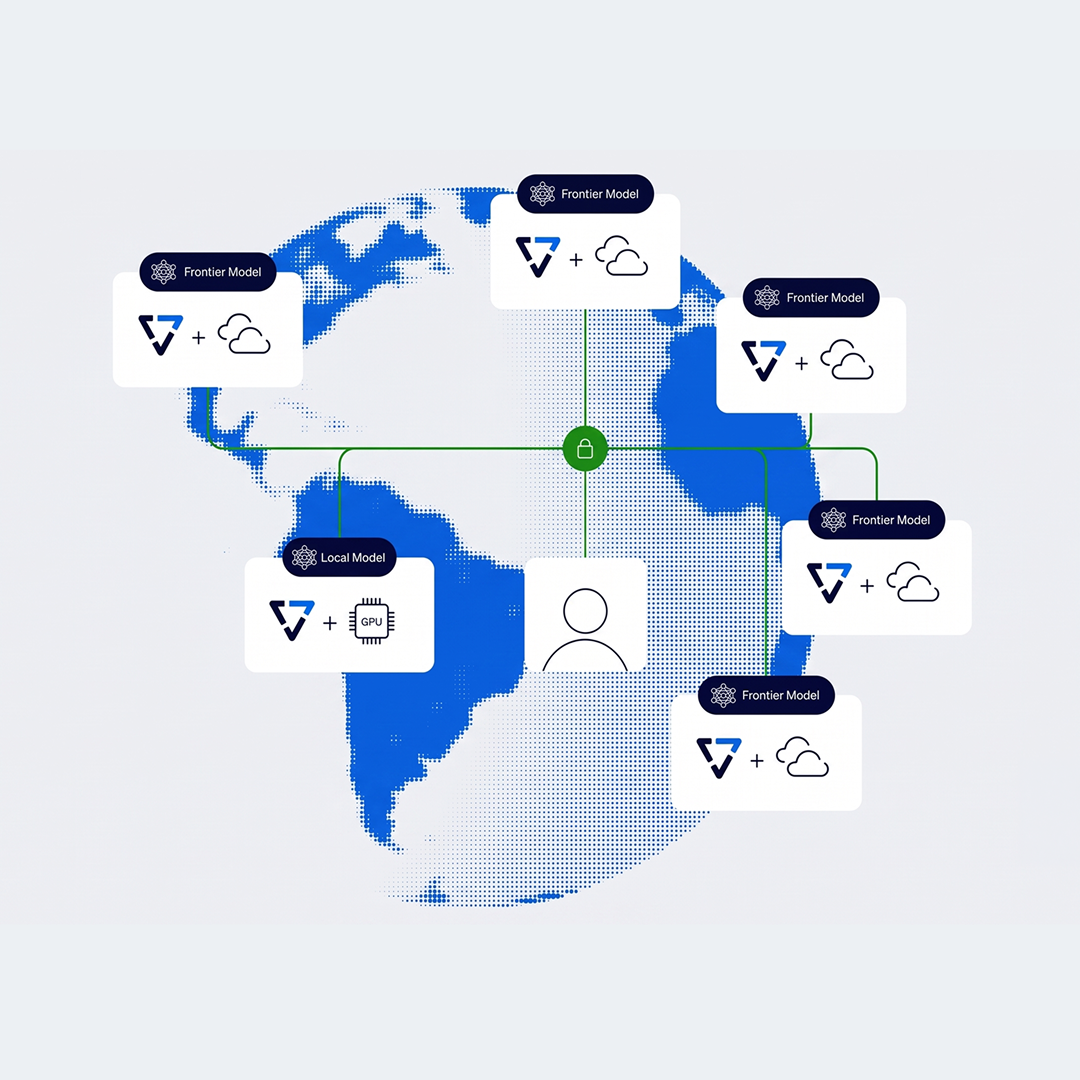
For OEMs: Deliver Confidential AI Infrastructure
Deliver turnkey infrastructure with confidential compute, accelerated AI, and VAST data services pre-integrated to help customers deploy protected AI environments at scale.