
Governance Can No Longer Live Outside the Data
Compliance used to be a perimeter and a process. Put regulated data in a system of record. Wrap it in access reviews and retention policies. Let a quarterly audit confirm the wrapper held. The data sat still long enough for the process to catch up.
Then AI started moving that same data continuously, from source systems into warehouses, into vector indexes for retrieval, into streaming tiers for real-time features, and into GPU clusters for training. Every hop is another copy, another credential, another jurisdiction. A governance layer that sits apart from the data cannot see any of it, let alone control it.
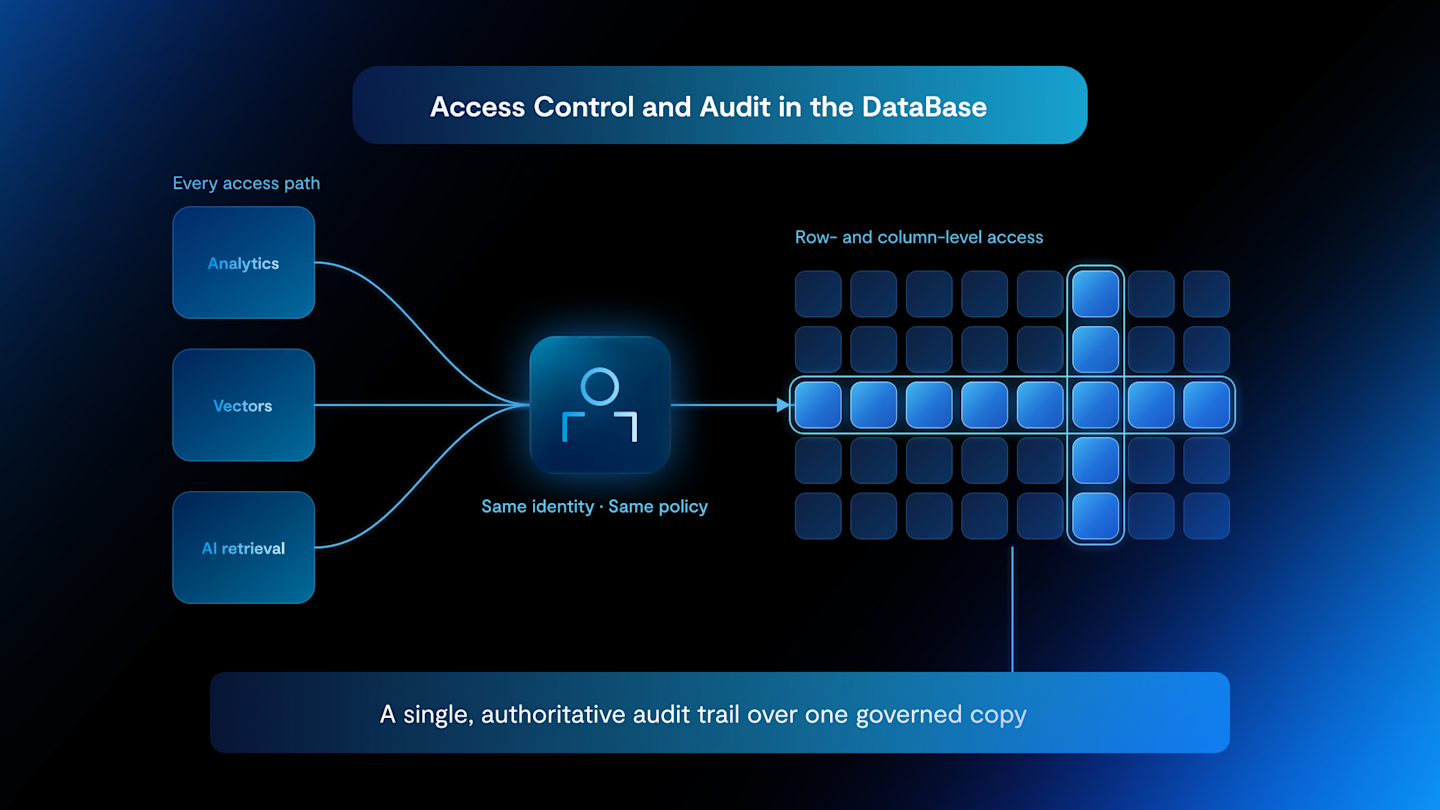
VAST puts the control inside the data. The Disaggregated and Shared-Everything (DASE) architecture keeps files, objects, tables, streams, and vectors as native Elements in one global namespace, so there is one authoritative copy to govern rather than many drifting duplicates. Encryption at rest, immutable snapshots, fine-grained access control, and audit stop being external wrappers and become behaviors of the data itself. Row- and column-level access is evaluated at the data layer against the same identity and policy for every access path, whether a query, a model retrieval, or an agent call, and access and changes are auditable over that one governed copy.
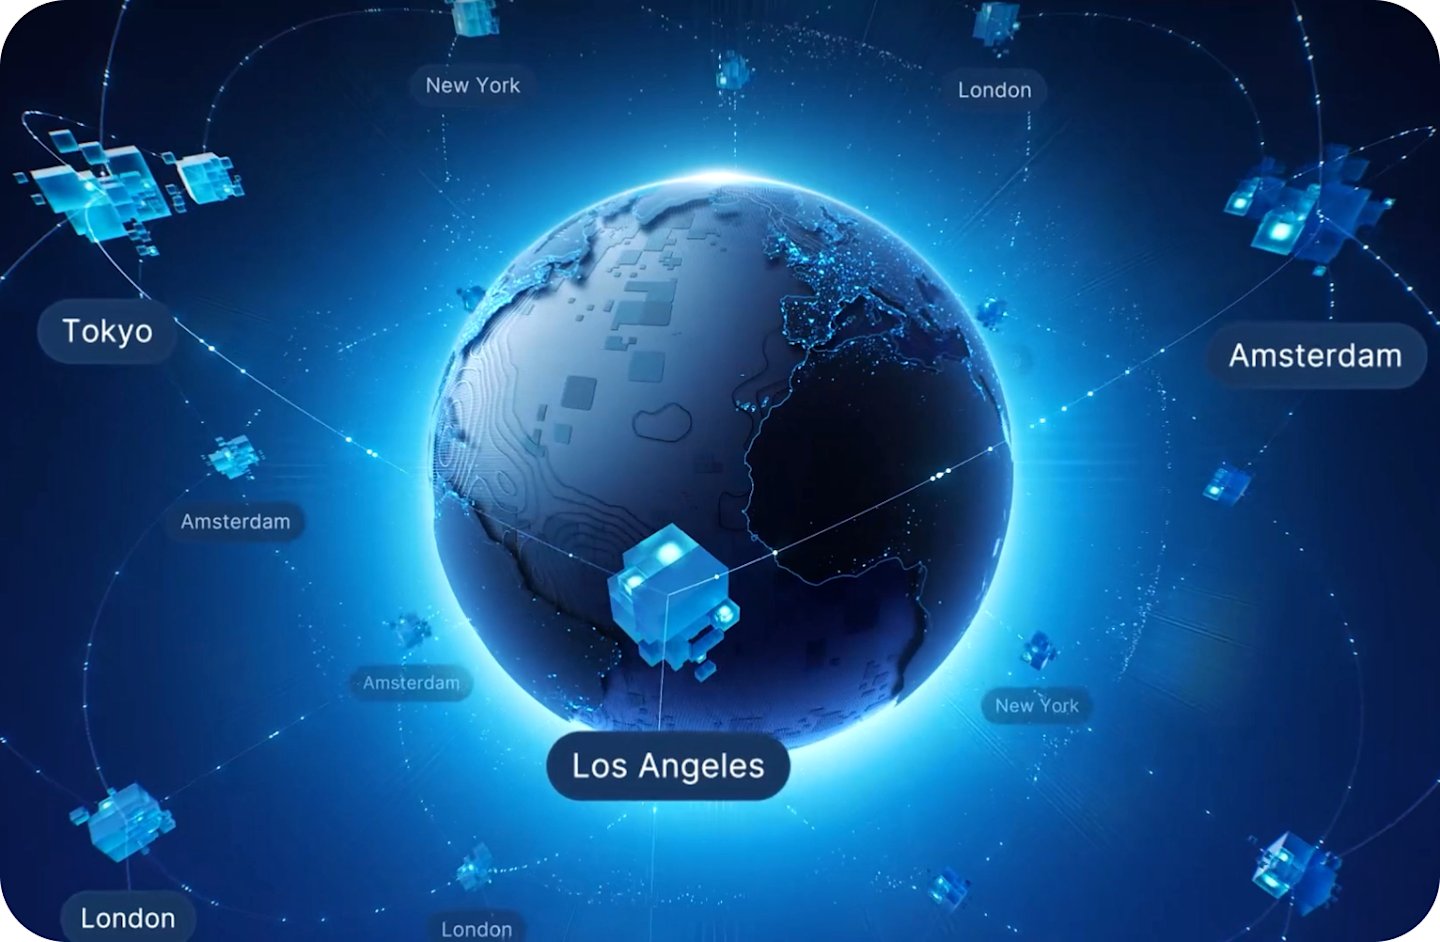
Now the control moves with the data. Analyst query, model retrieval, or agent action, the same policy, the same audit trail, and the same residency rules apply everywhere the record goes.