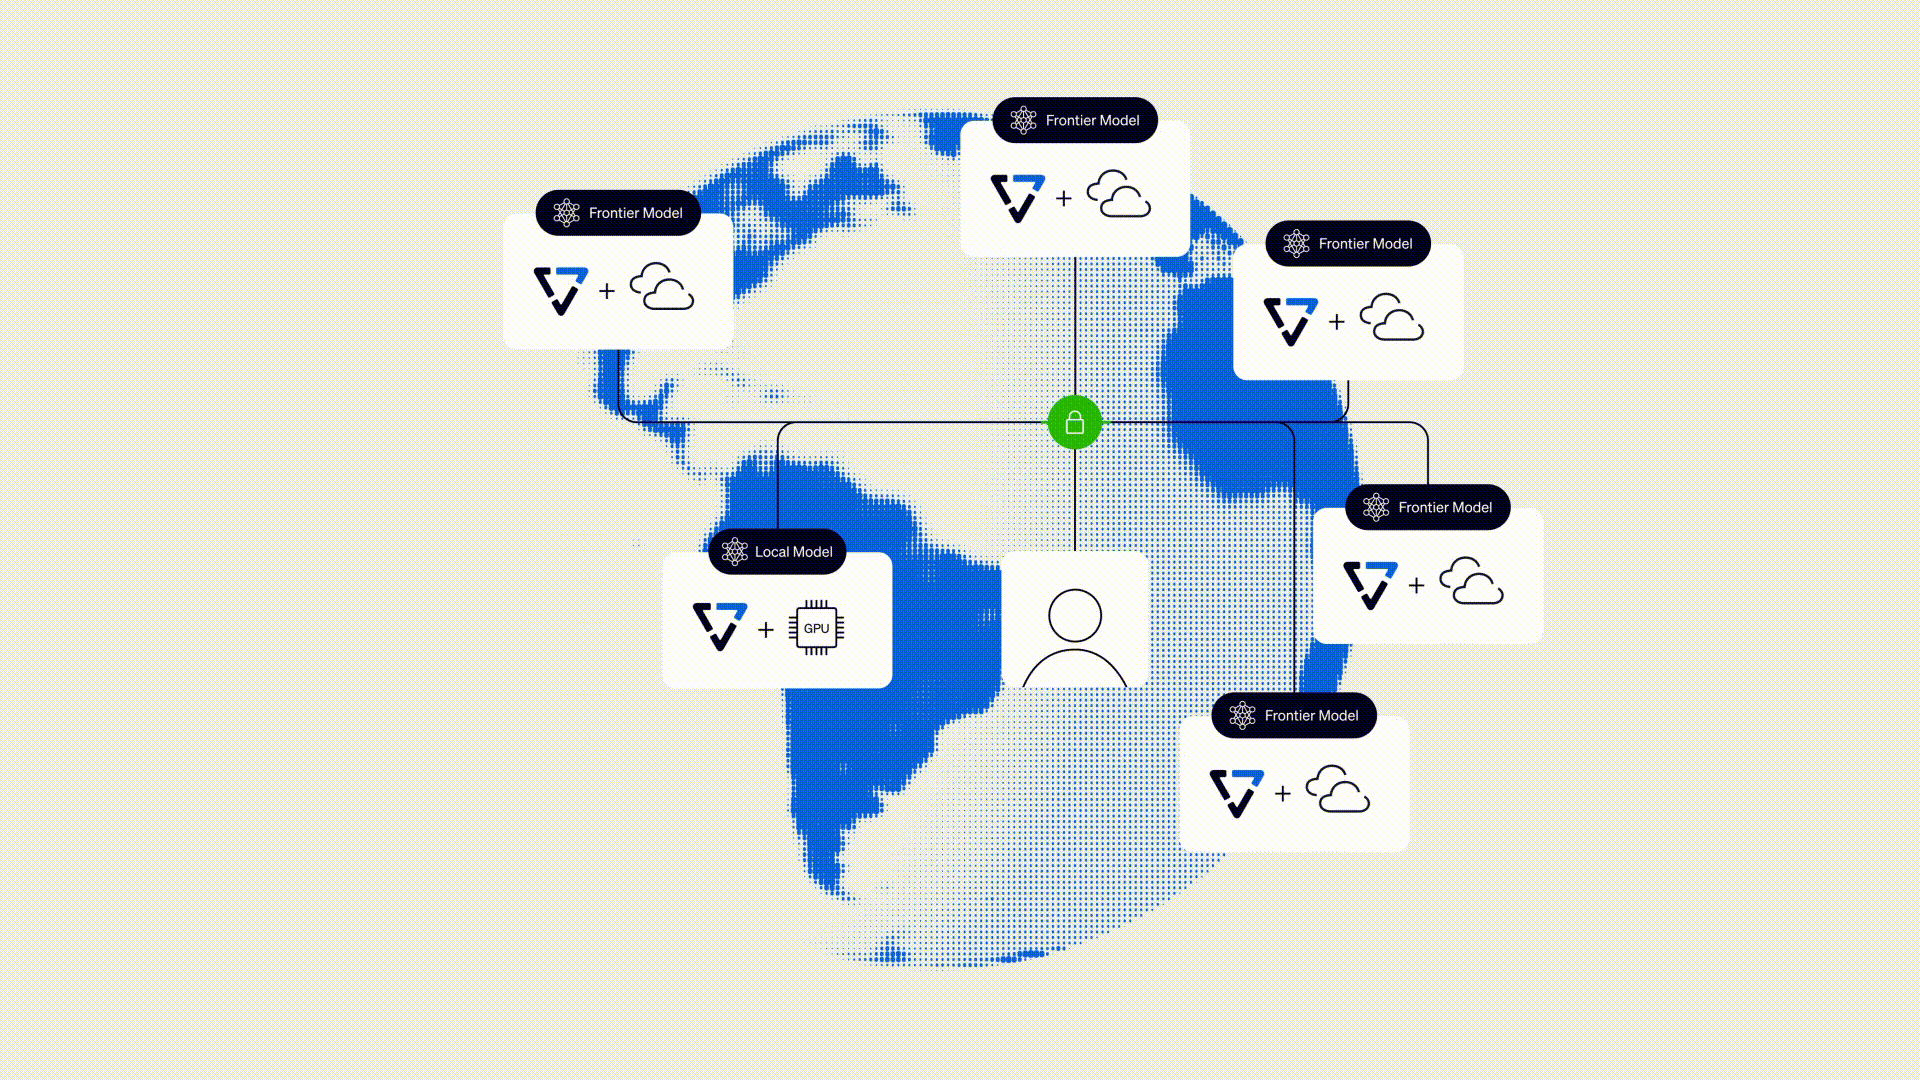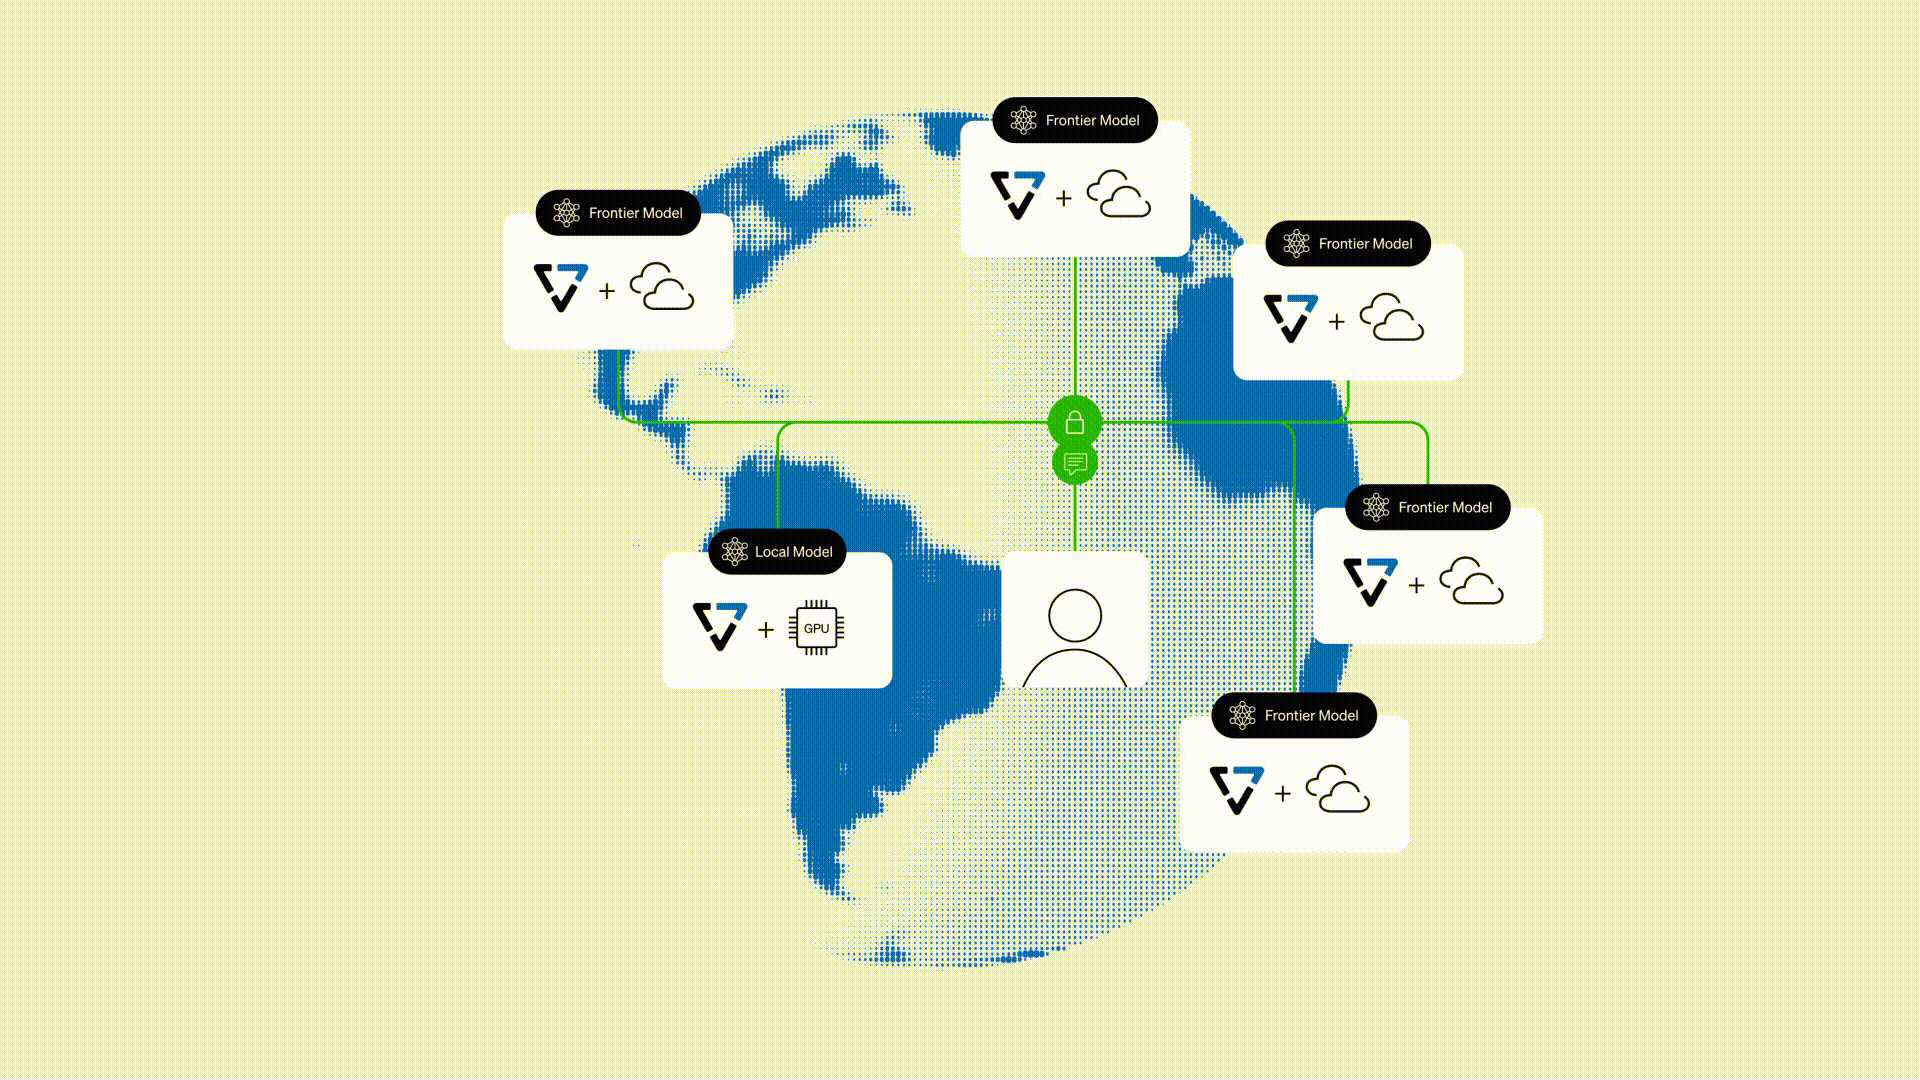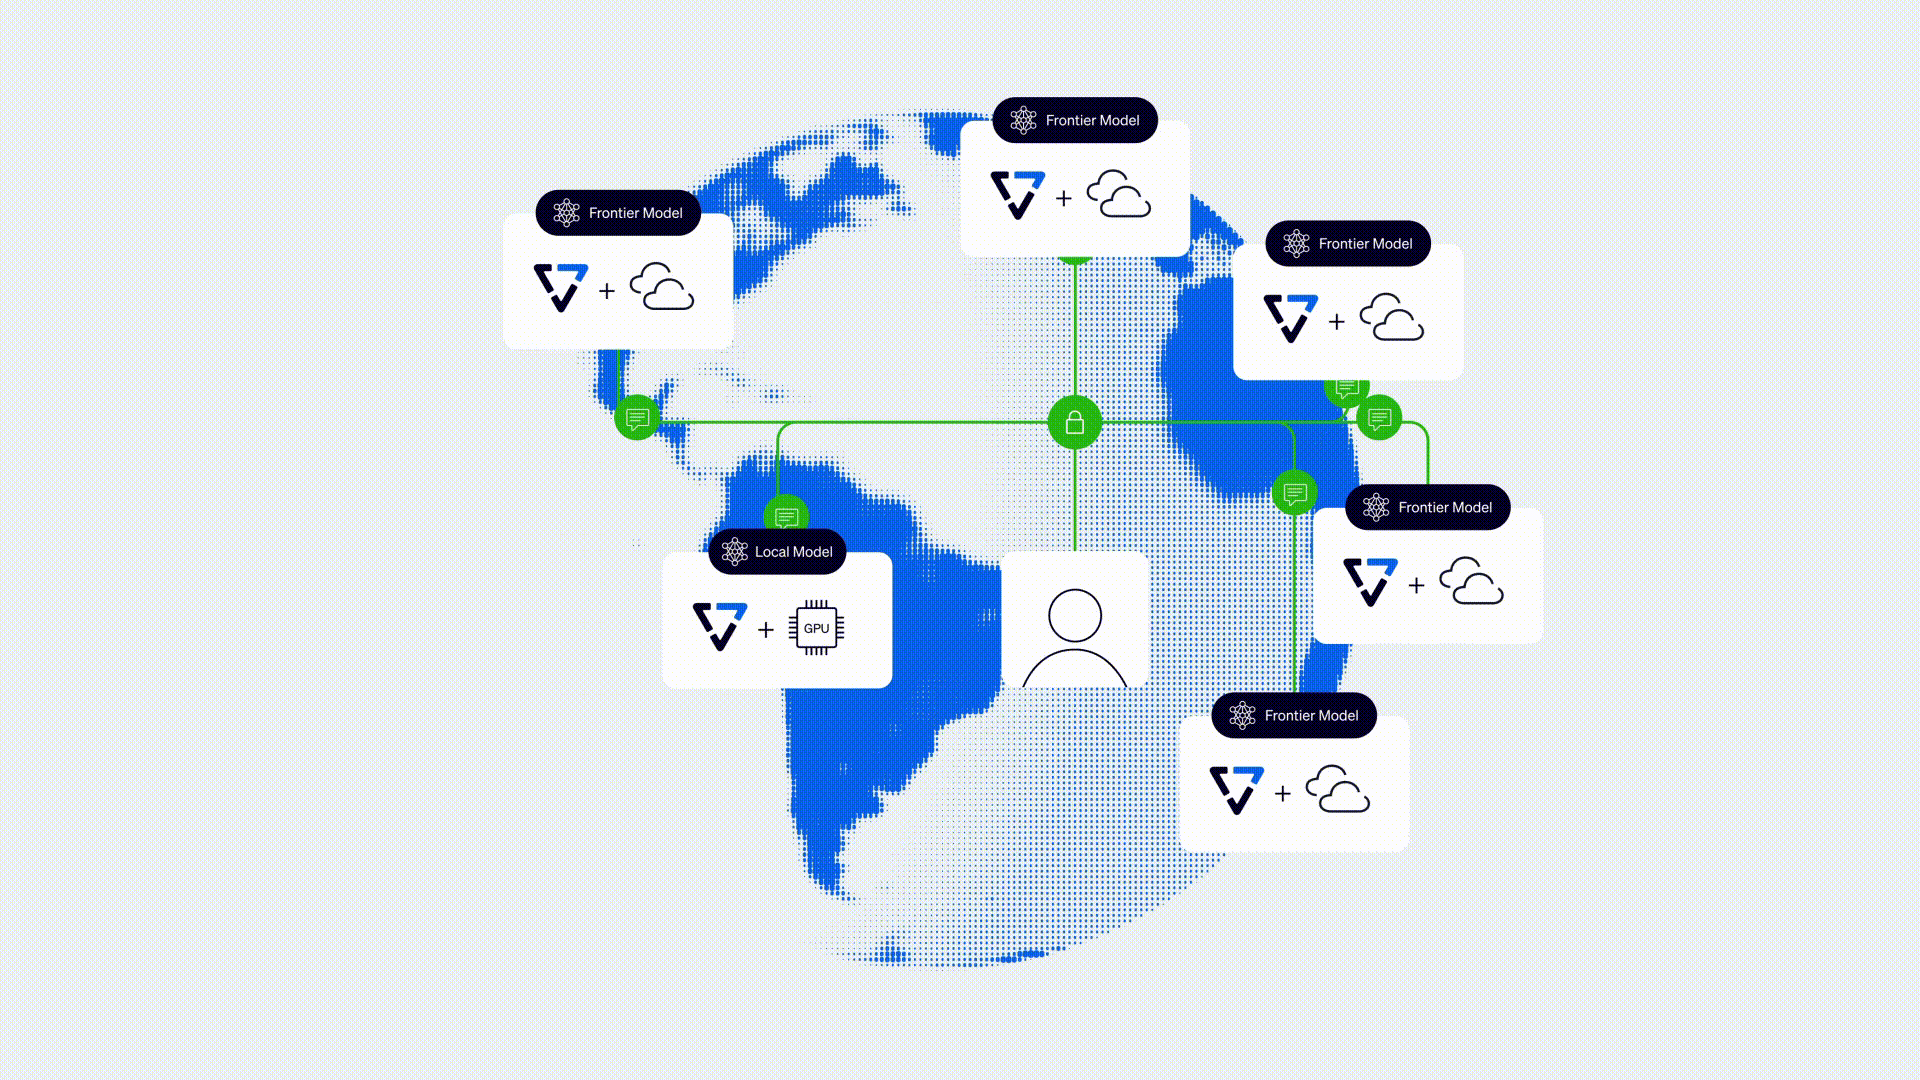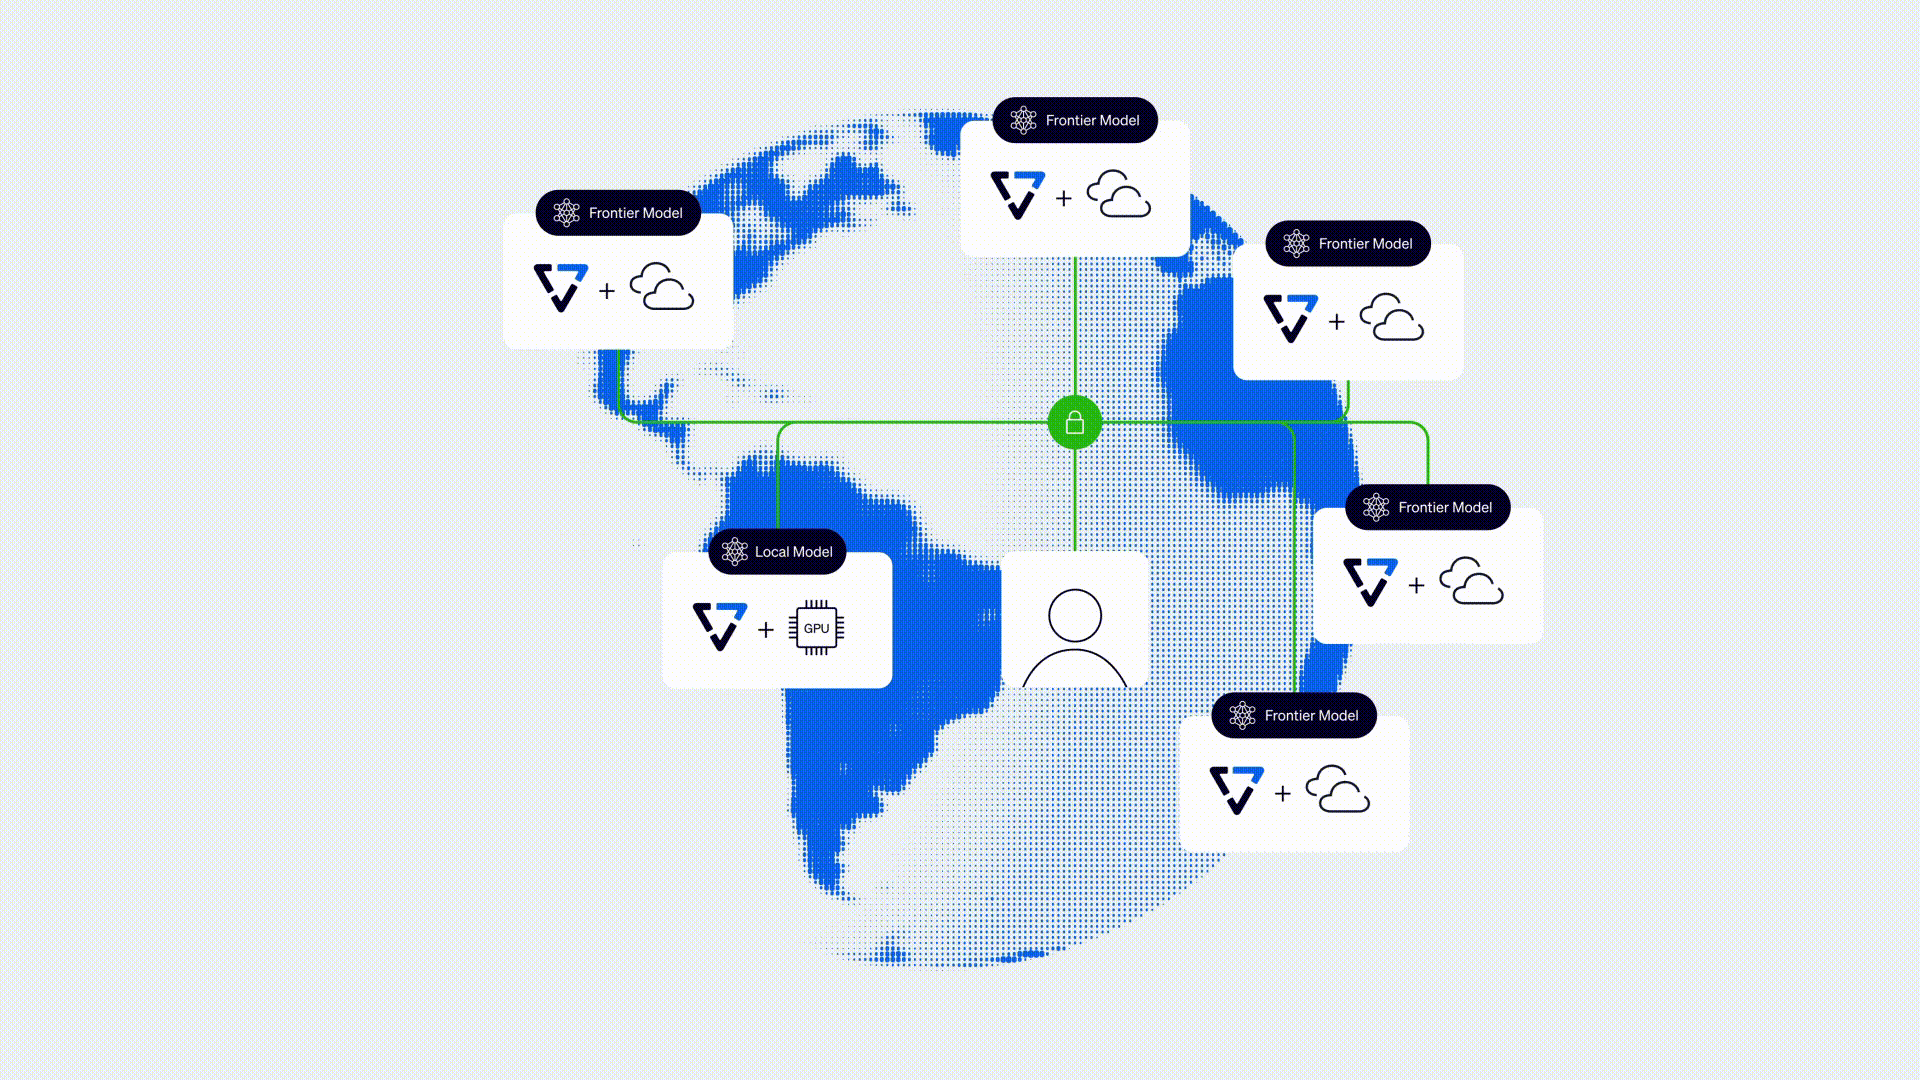
Bring frontier AI to sensitive enterprise data while preserving control of data, model IP, and infrastructure across the ecosystem.
VAST DataEnclave
Bring State-of-the-Art AI to the World’s Most Sensitive Data
Run advanced AI on regulated data while protecting enterprise data and proprietary models with verified, hardware-isolated confidential execution.
AI Trust Challenges
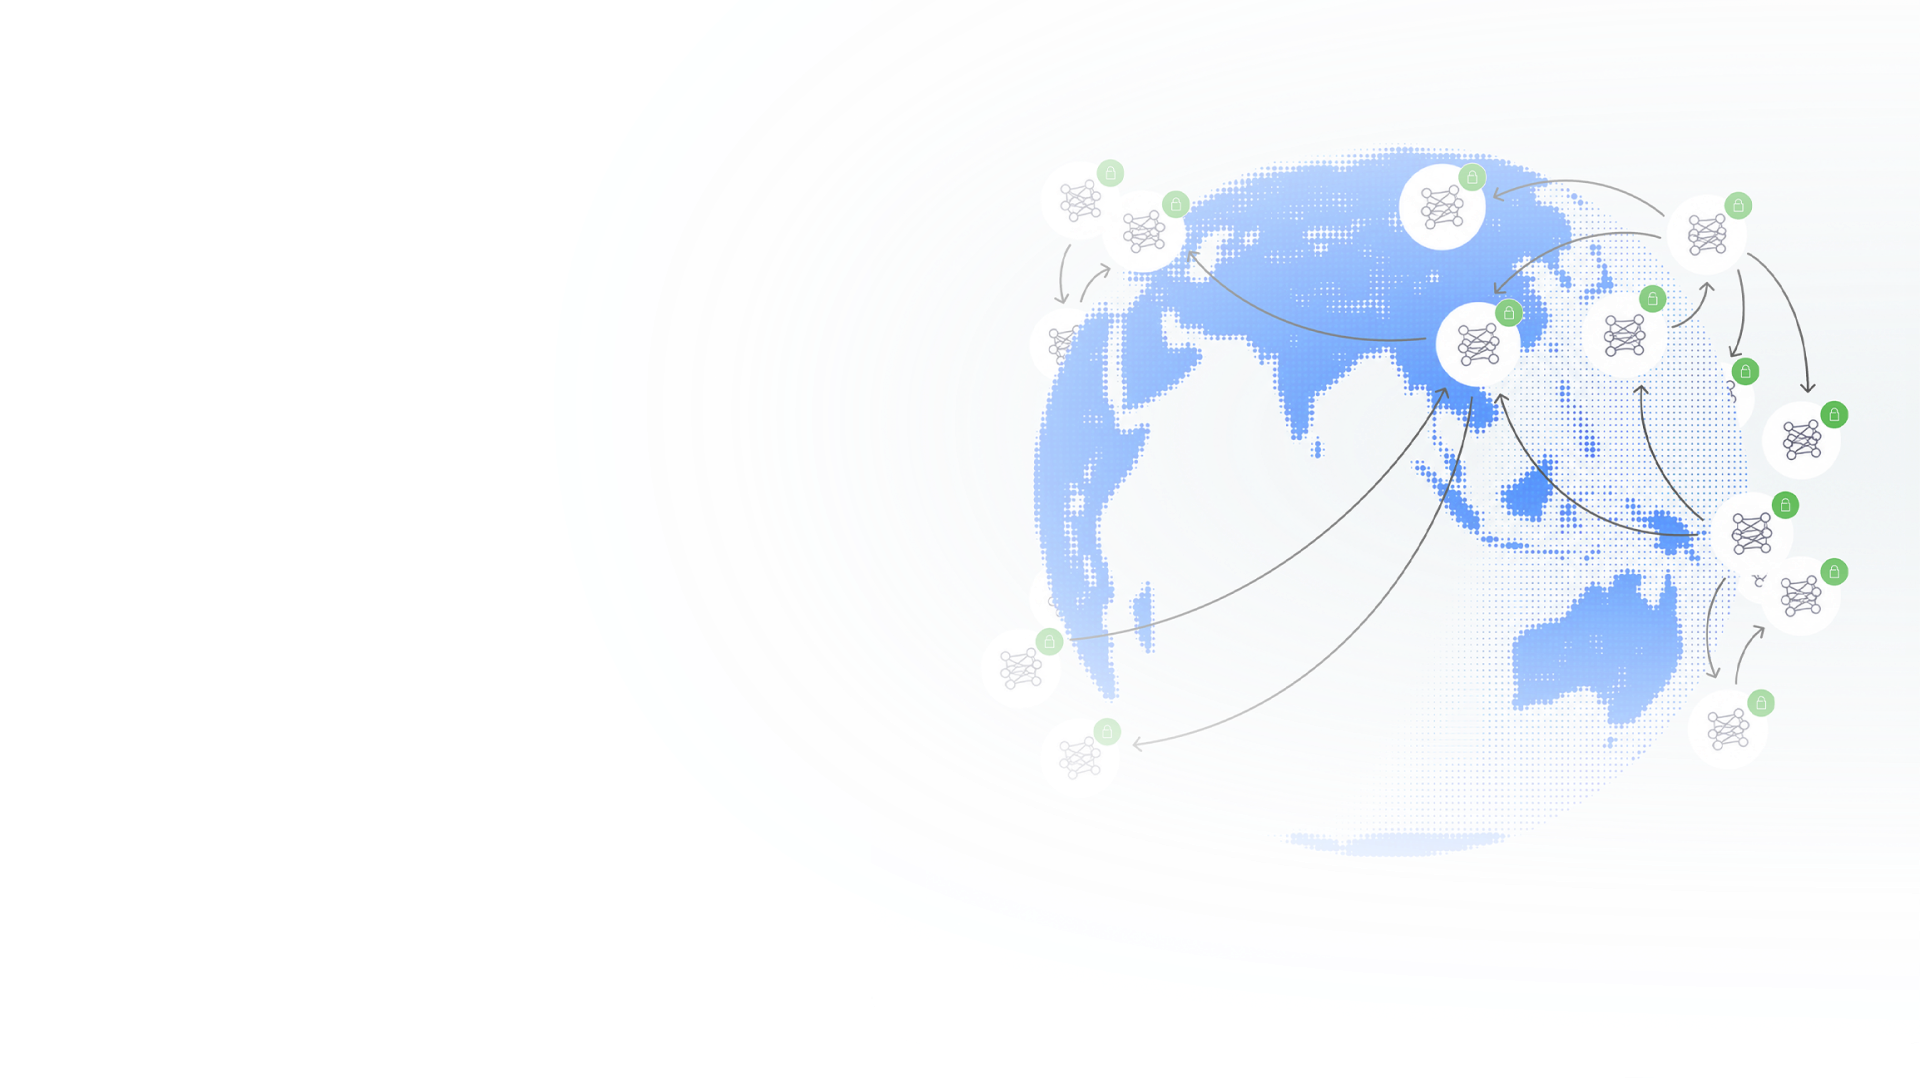
When Sensitive Data and Advanced AI Can’t Meet
Enterprises need frontier AI without exposing sensitive or regulated data. Model providers need a secure way to bring their proprietary, closed-weights models to those customers without exposing their intellectual property.
Strict Data Boundaries
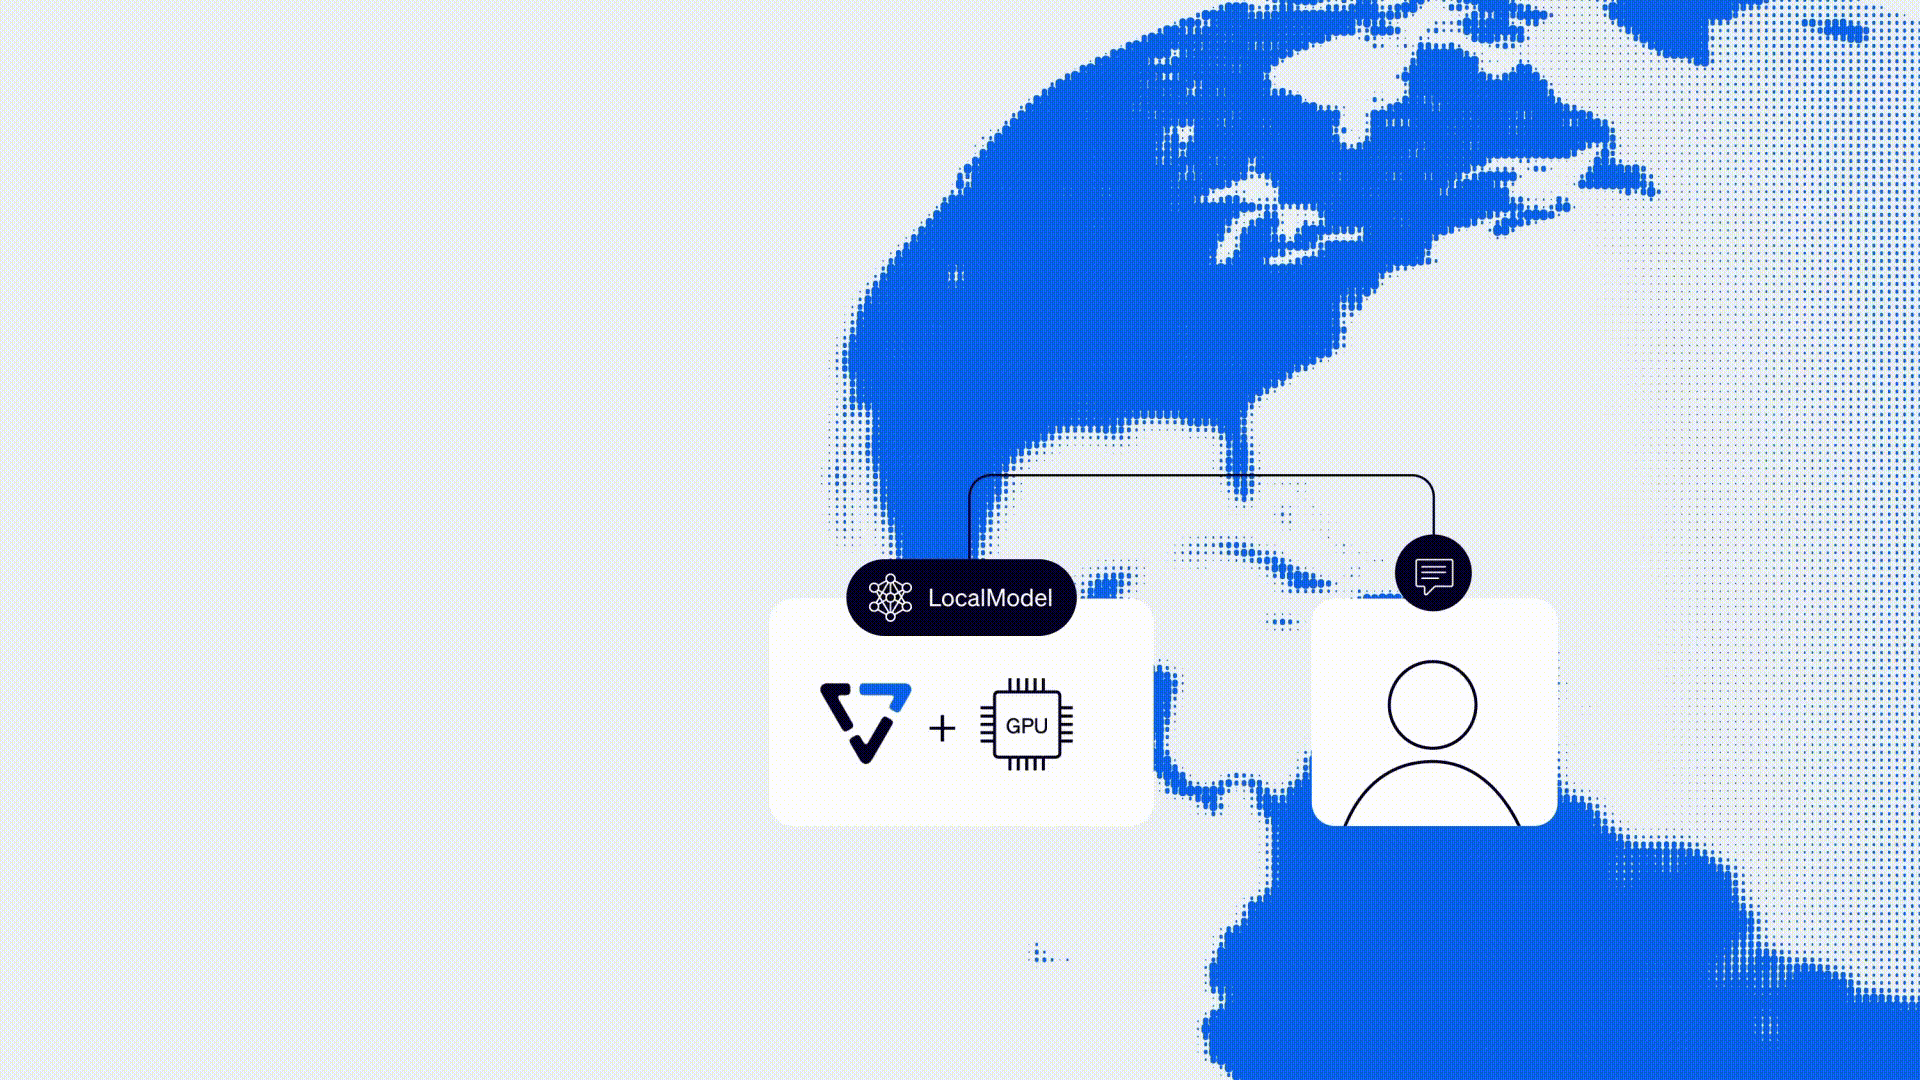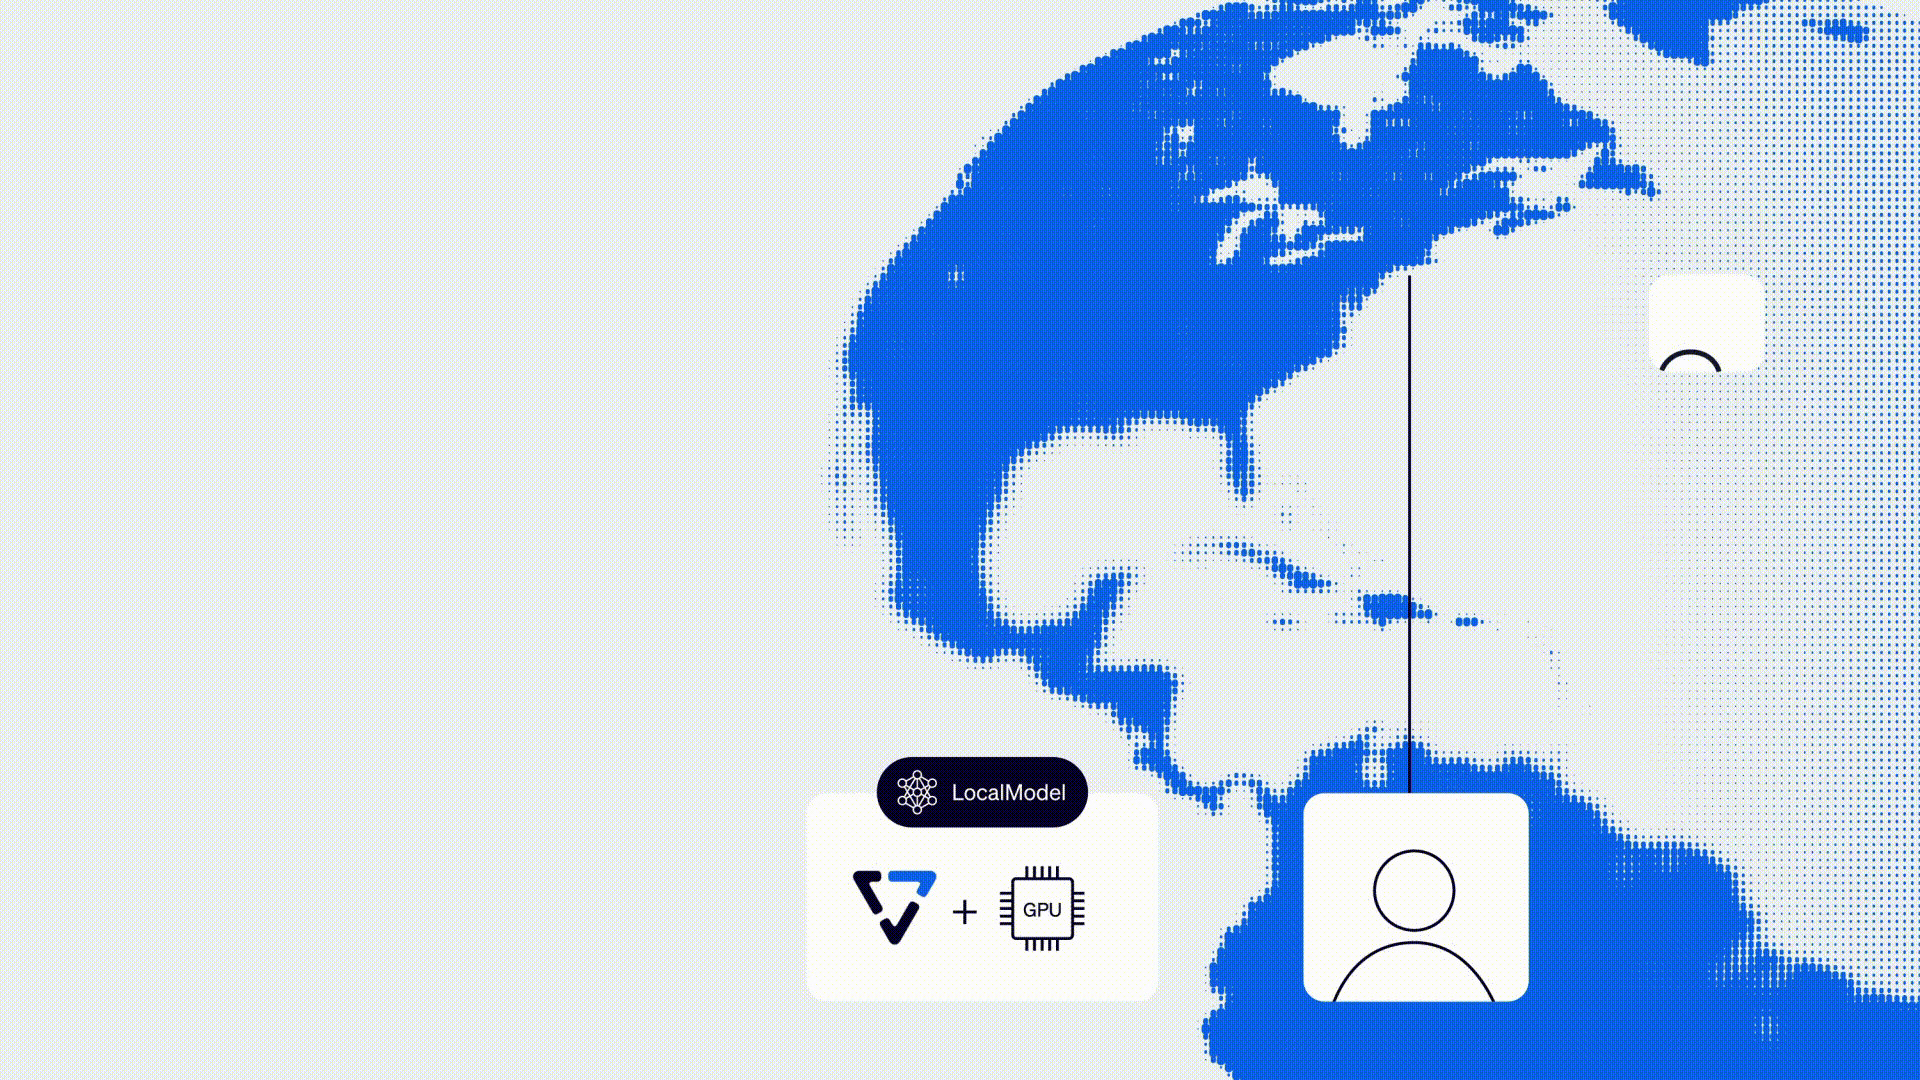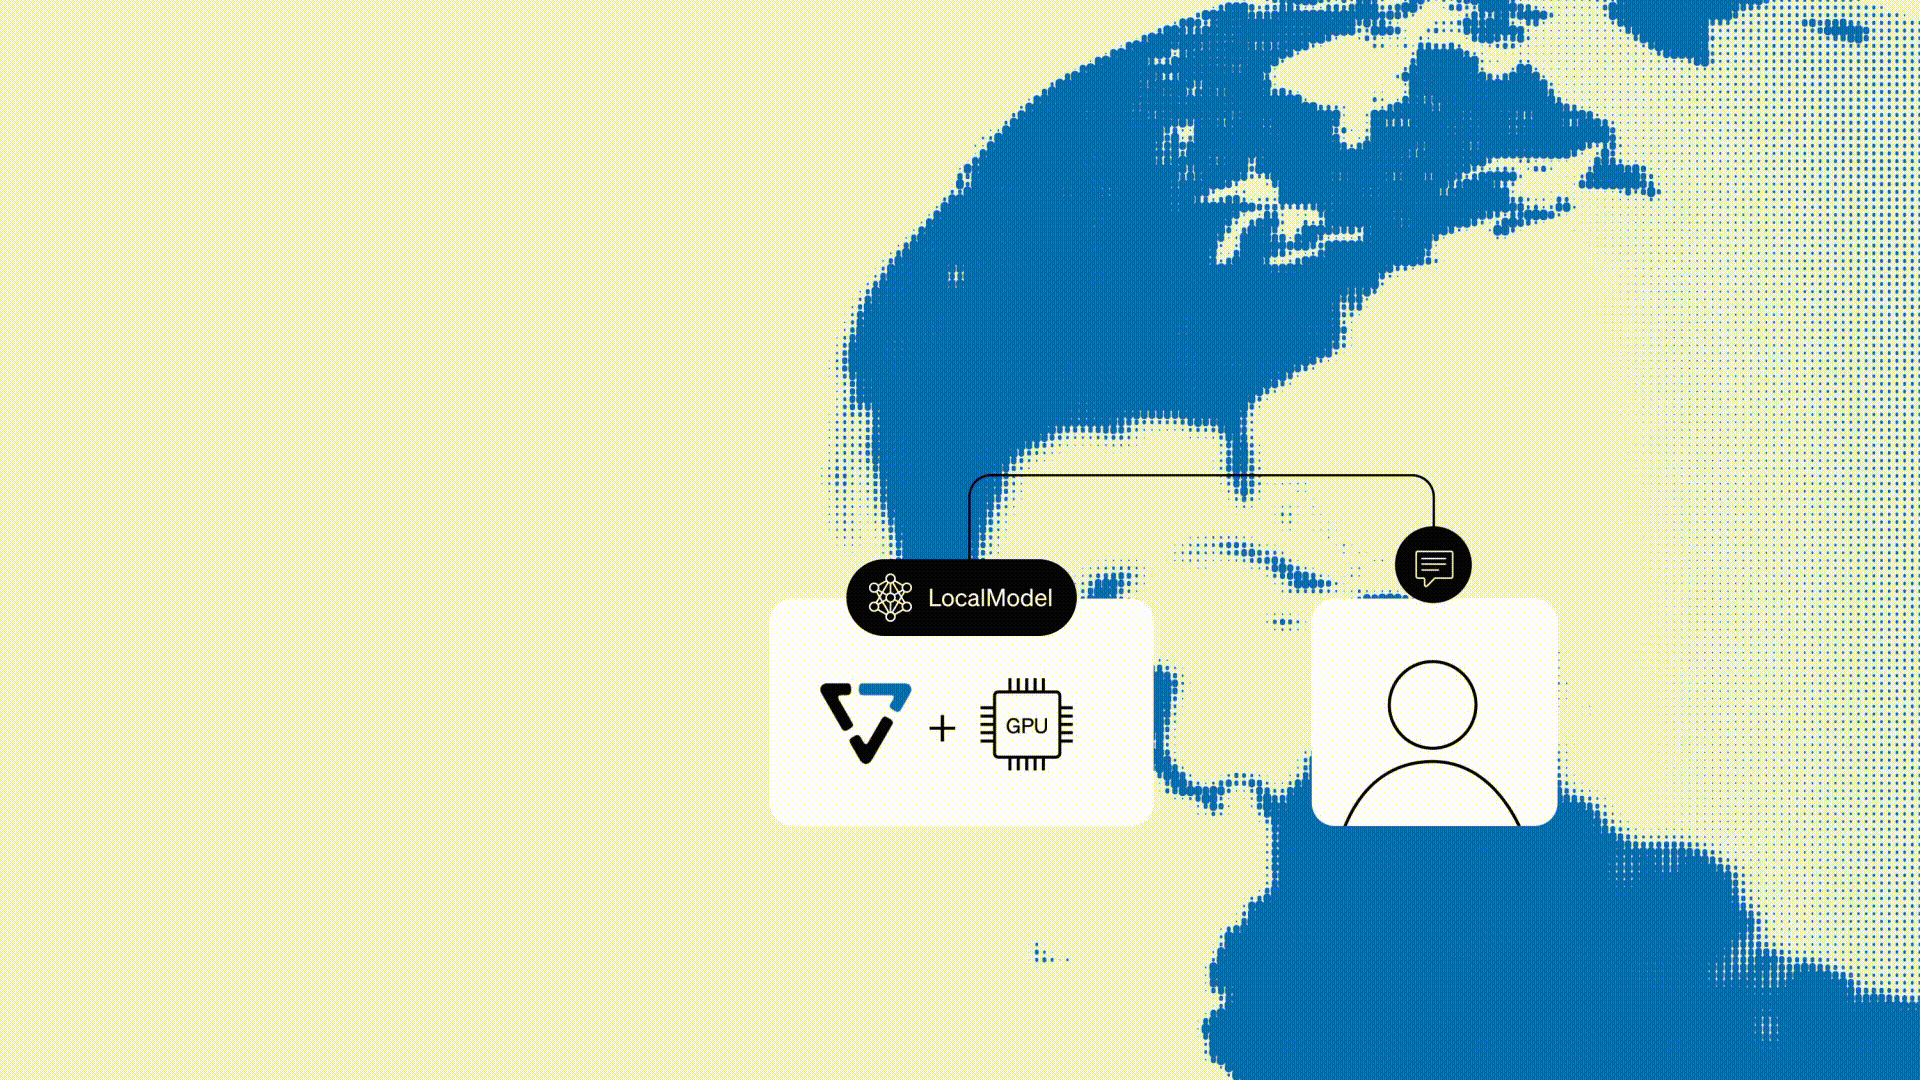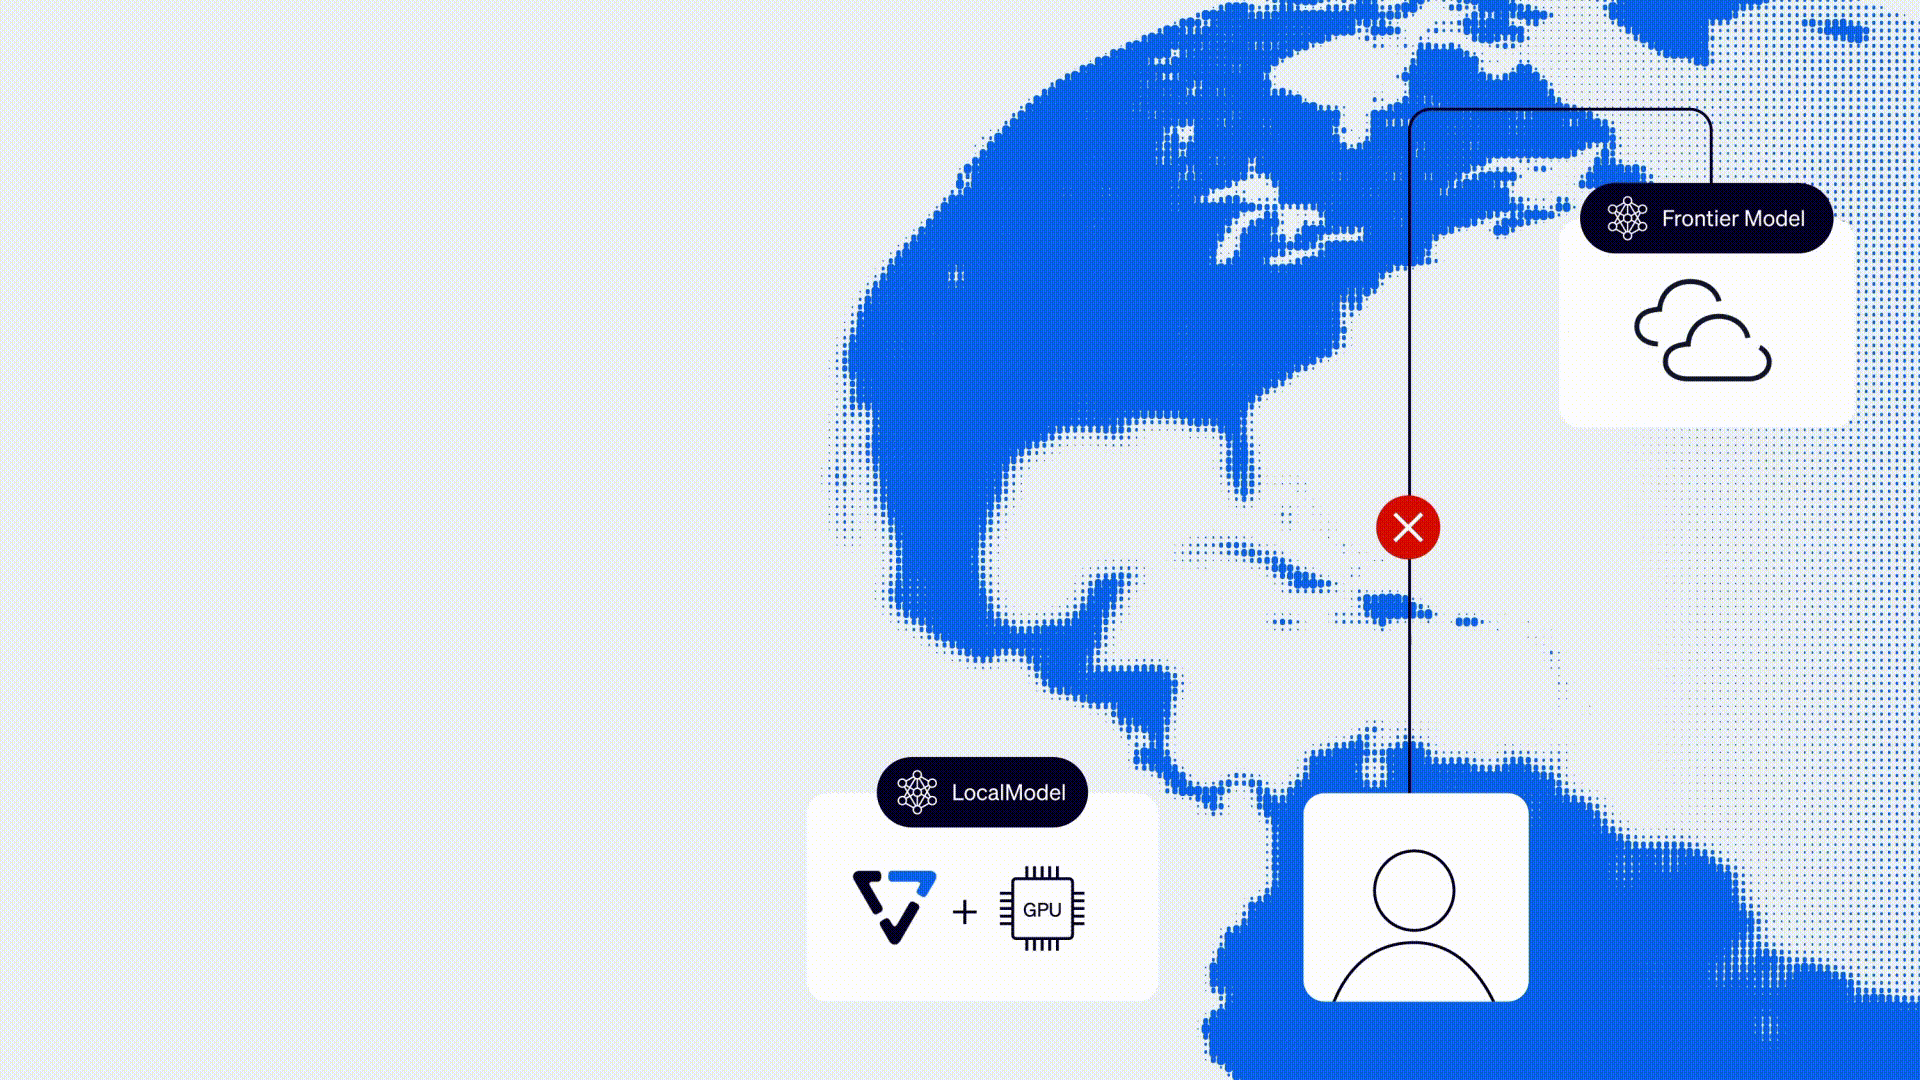
Regulatory, sovereignty, and security requirements prevent sensitive enterprise data from moving outside controlled environments. DataEnclave brings proprietary AI to the data while keeping it protected within the enterprise security domain.
Read the blog
Core Capabilities
A Trusted Environment for Enterprise AI
VAST DataEnclave protects sensitive data and proprietary models while AI is running, creating a secure, verified environment where enterprises and model providers can securely collaborate.
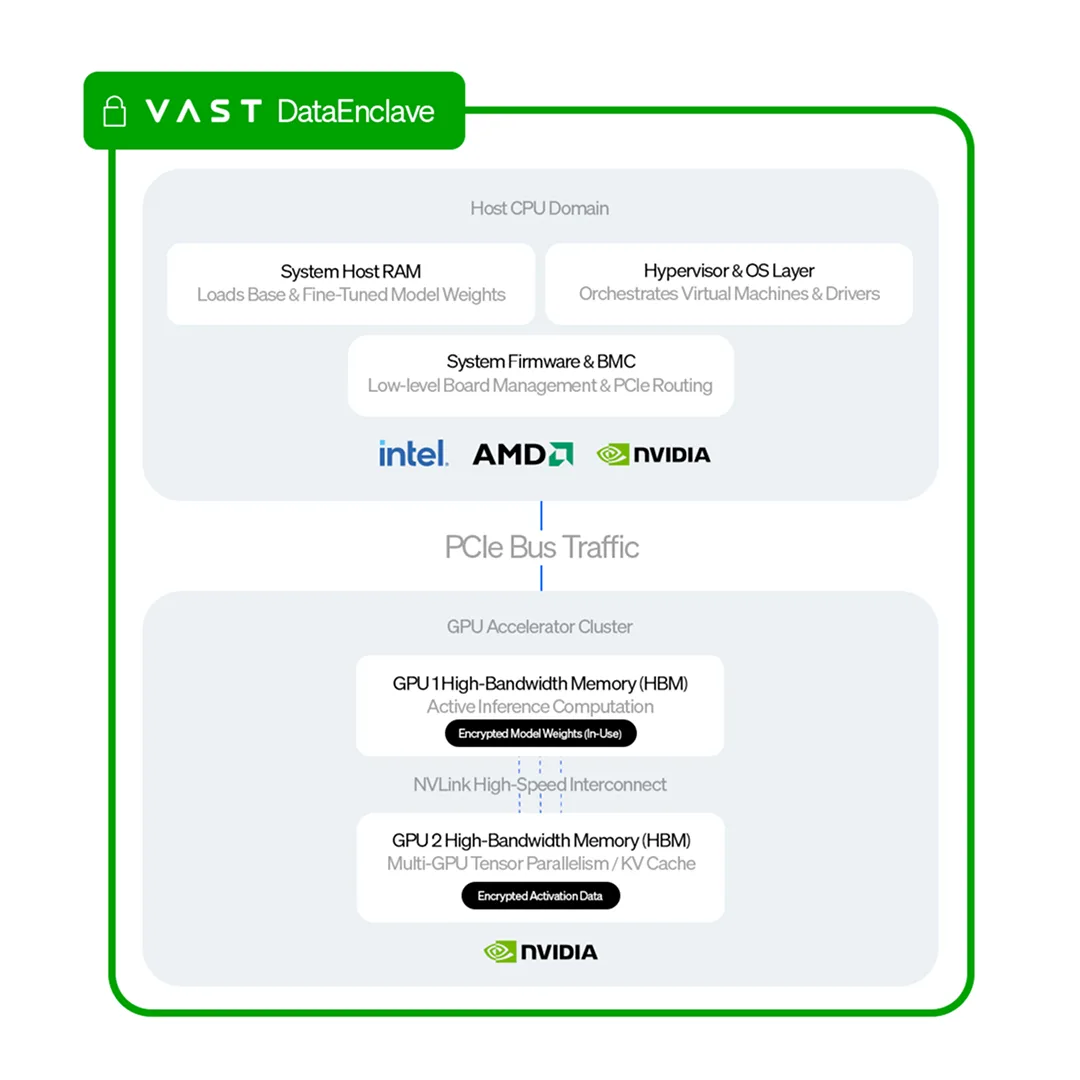
Hardware-Isolated Execution
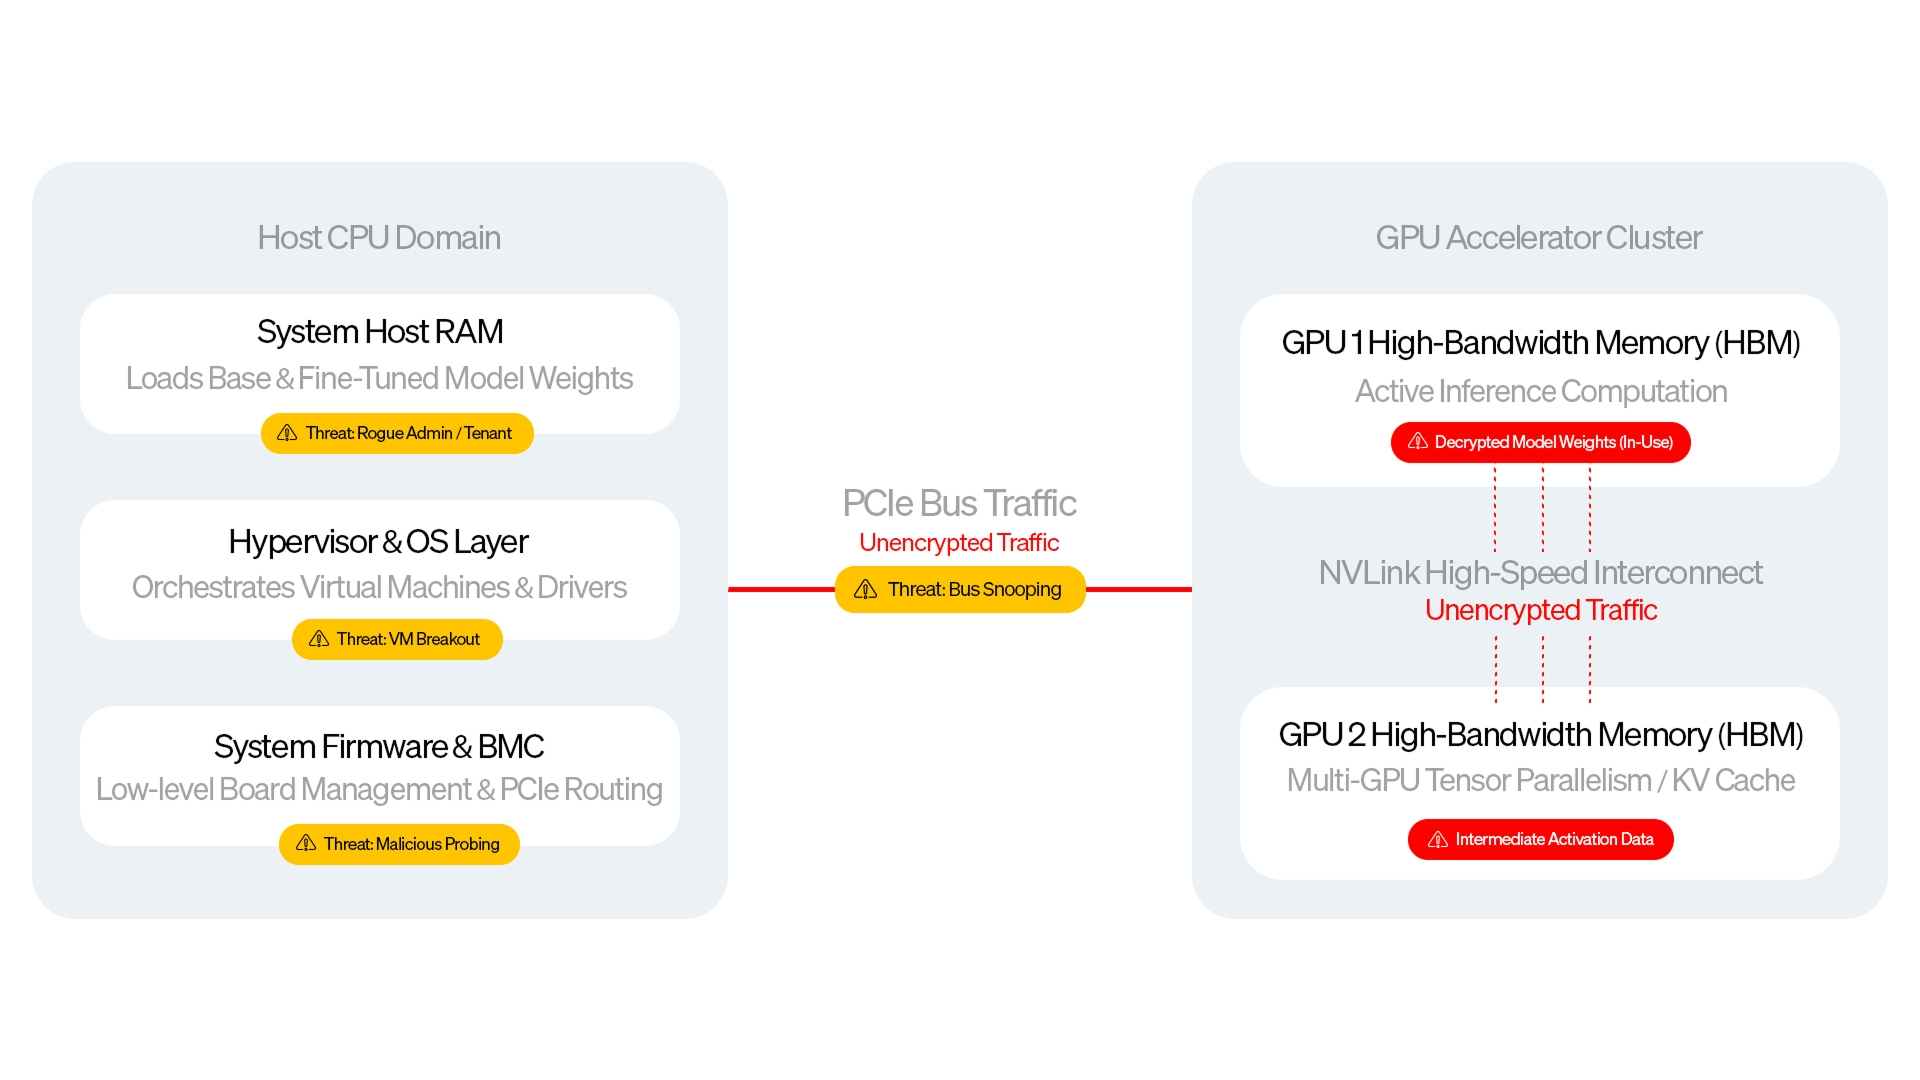
Run AI workloads inside hardware-isolated confidential environments that protect sensitive data and models while in action, isolating them from the underlying infrastructure and privileged operators.
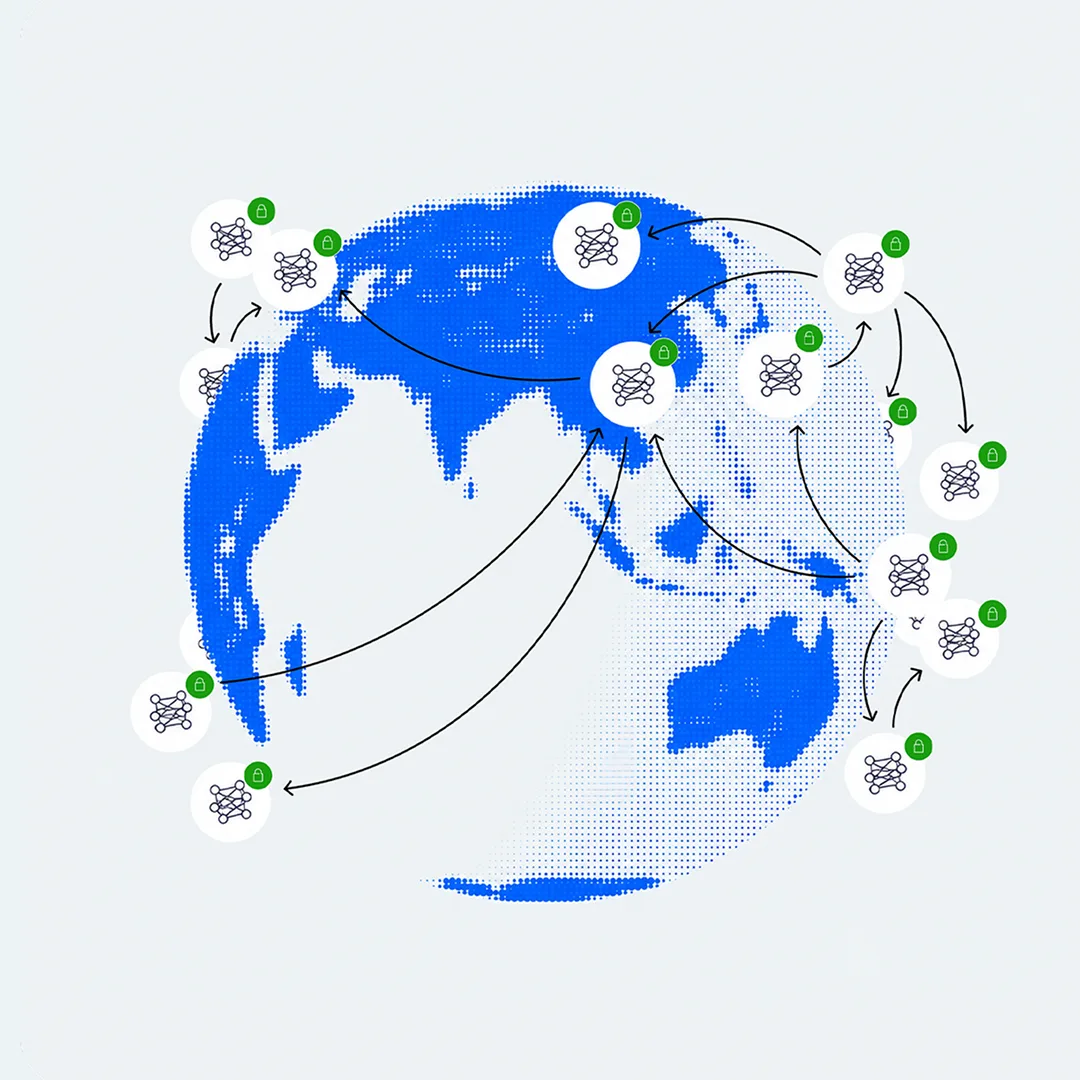
Verify Before Decrypt
Cryptographically verify the hardware, software environment, and workload policy against approved security requirements before protected assets become accessible, ensuring data and models remain protected in untrusted environments.
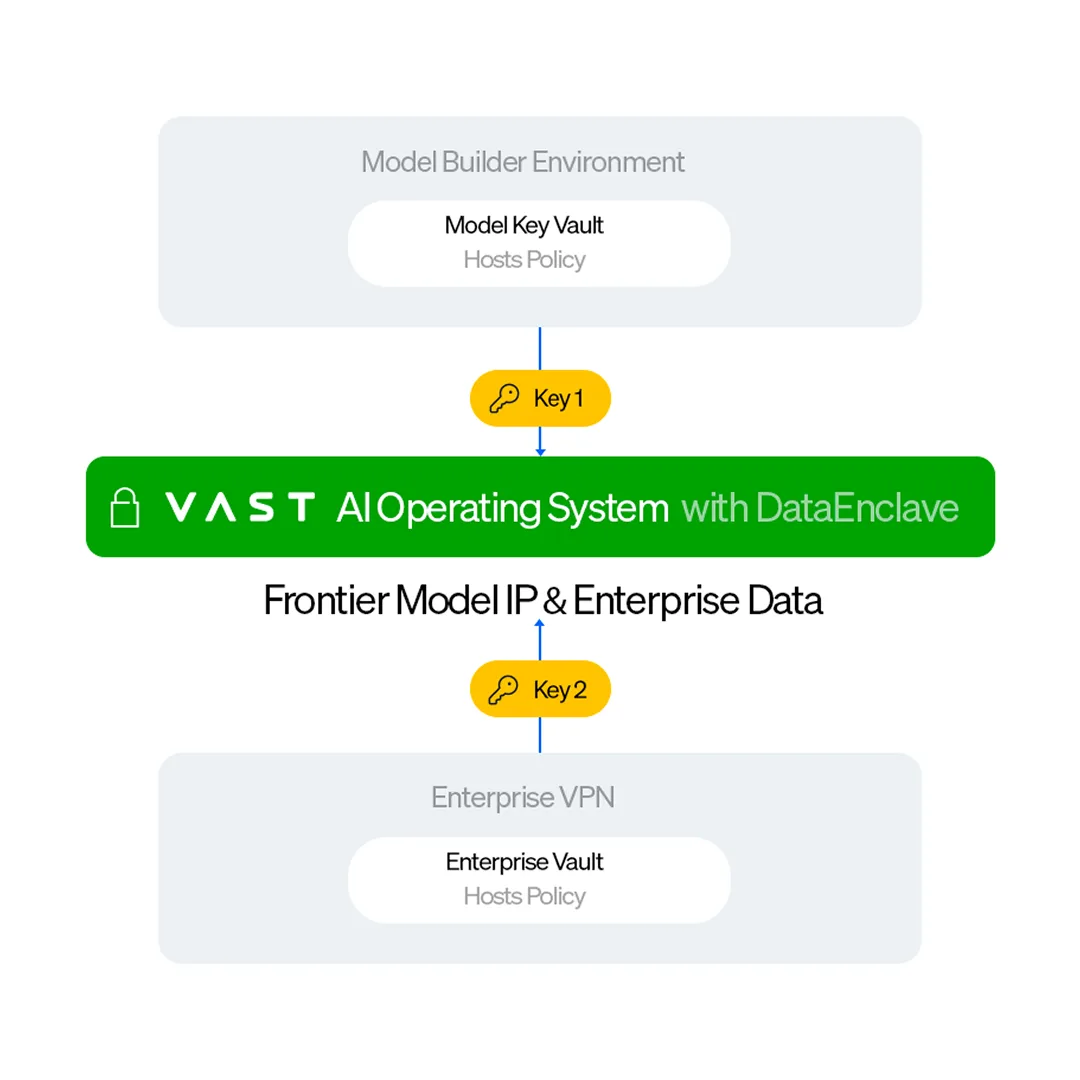
Independent Key Ownership
Keep enterprise data and proprietary model weights protected under their respective owners’ control. VAST DataEnclave integrates with customer-controlled and third-party key management infrastructure so each party retains authority over its protected assets.
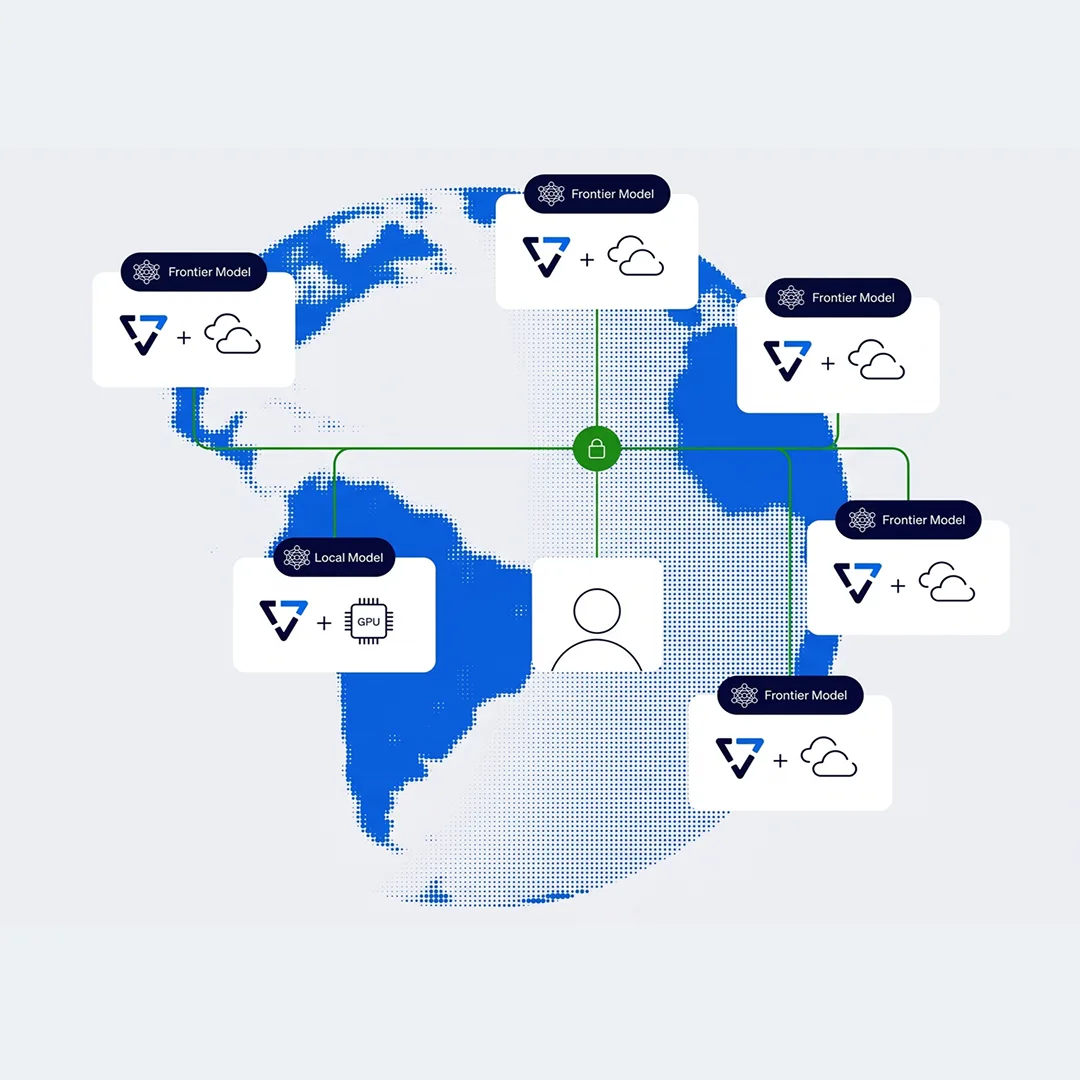
Connected or Air-Gapped
Deploy confidential AI across connected, private, sovereign, and fully air-gapped environments while maintaining the same verify-before-decrypt trust model and security protections wherever sensitive data must remain.
Auditable by Design
Maintain a tamper-proof audit trail of attestation, key releases, policy decisions, and workload activity, providing security and compliance visibility without exposing protected data or model assets.
Product Benefits
Build a Confidential AI Factory
For Enterprises: Use Advanced AI on Sensitive Data
Run proprietary foundation models and fine-tuned AI against regulated data inside the enterprise security domain, bringing advanced AI to sensitive workloads without sending protected datasets to externally hosted model services.
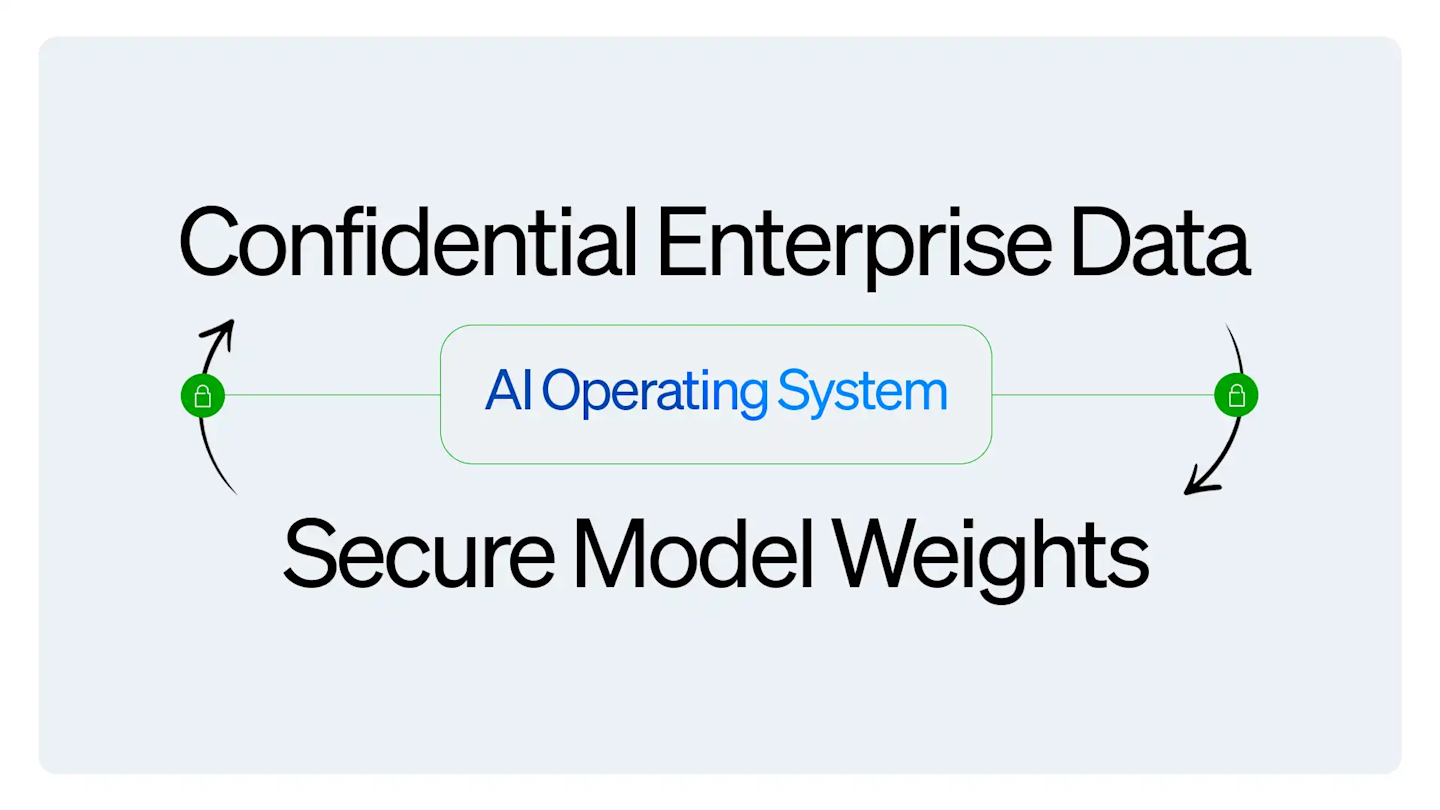
Model Builders: Protect Proprietary Model IP
Bring proprietary, closed-weight models to sensitive enterprise workloads while keeping model assets protected and under the model provider’s control, enabling customers to use advanced models within their required security boundaries.
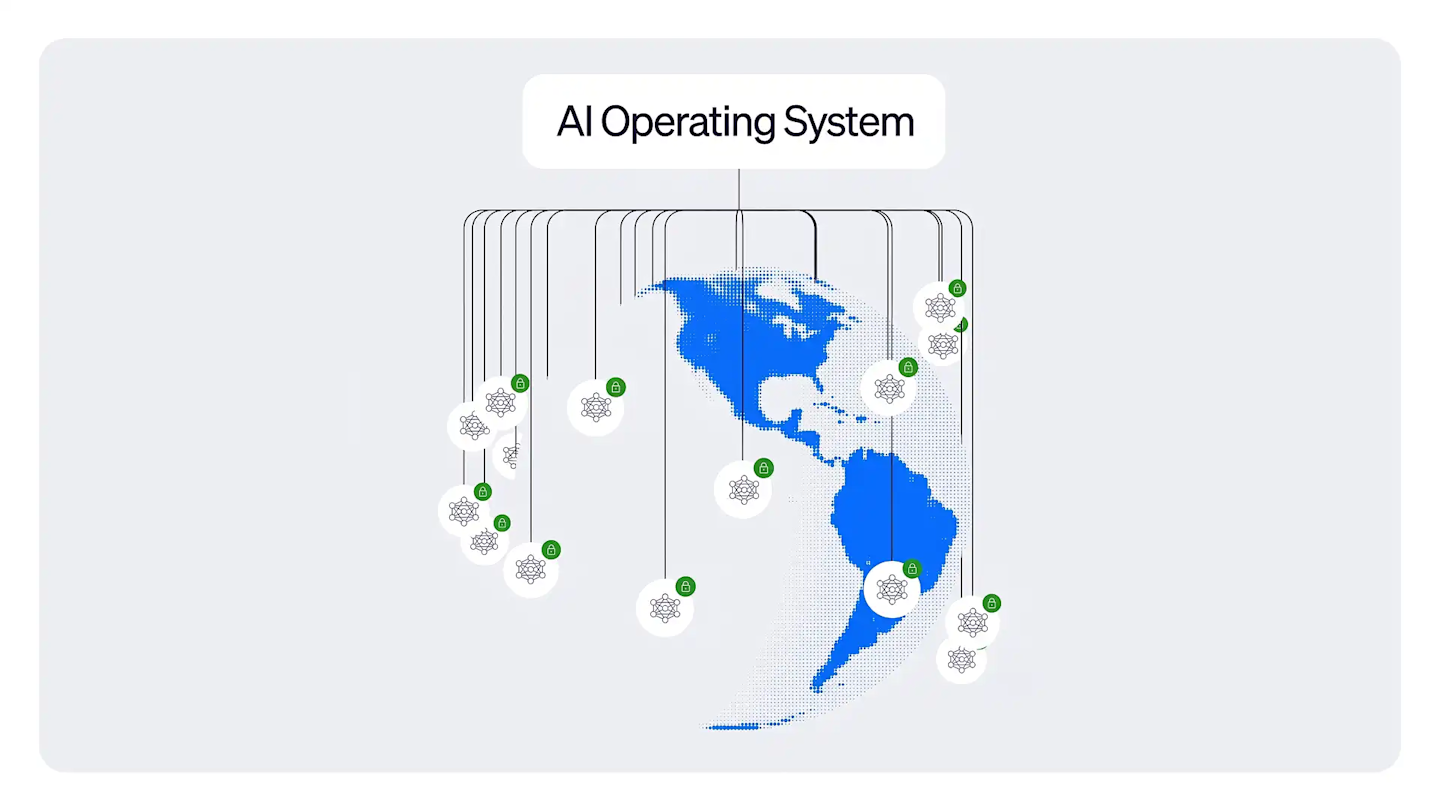
For AI & Sovereign Clouds: Protect Data and Models From Operators
Host proprietary models and regulated enterprise data without gaining access to either, enabling customers to run sensitive AI workloads on accelerated infrastructure while maintaining required security and sovereignty boundaries.
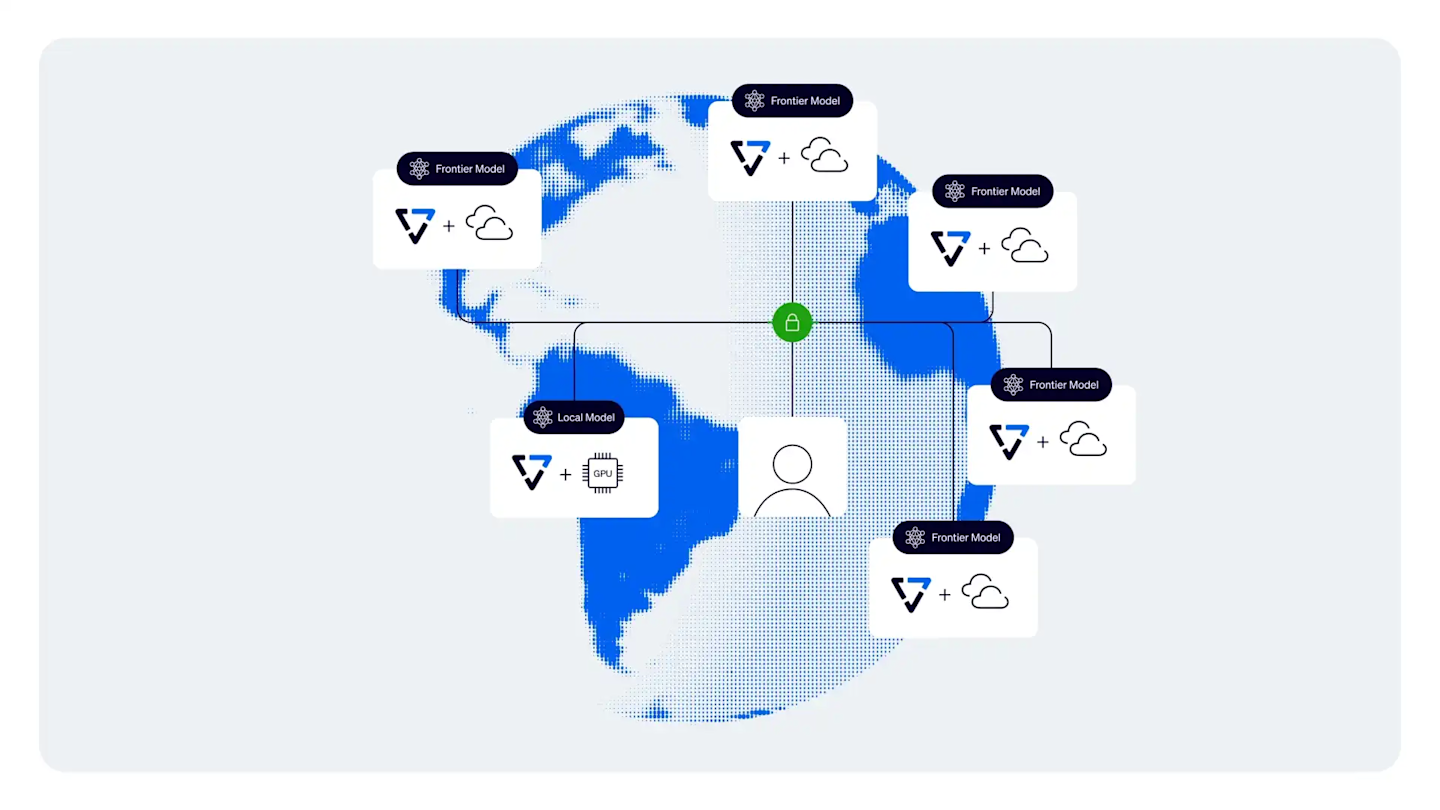
OEM Partners: Deliver Confidential AI Infrastructure
Deliver turnkey infrastructure with confidential compute, accelerated AI, and VAST data services pre-integrated, helping enterprises deploy protected AI environments designed to meet data and model owners’ security requirements.
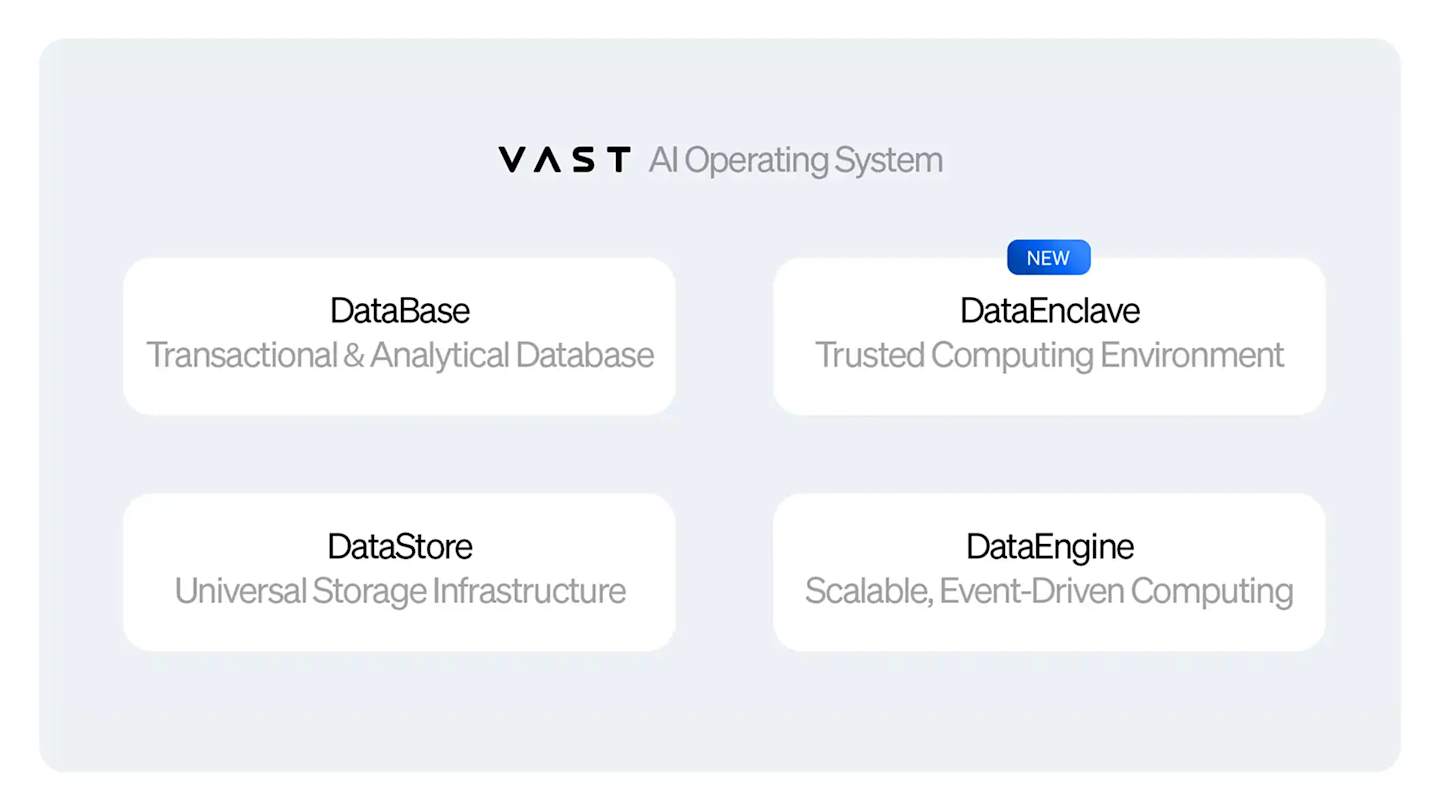
Build a Confidential AI Factory
VAST DataEnclave enables enterprises, model builders, AI cloud providers, and infrastructure partners to build confidential AI factories where state-of-the-art AI can operate on the world’s most sensitive data without requiring either the data owner or model owner to relinquish control.
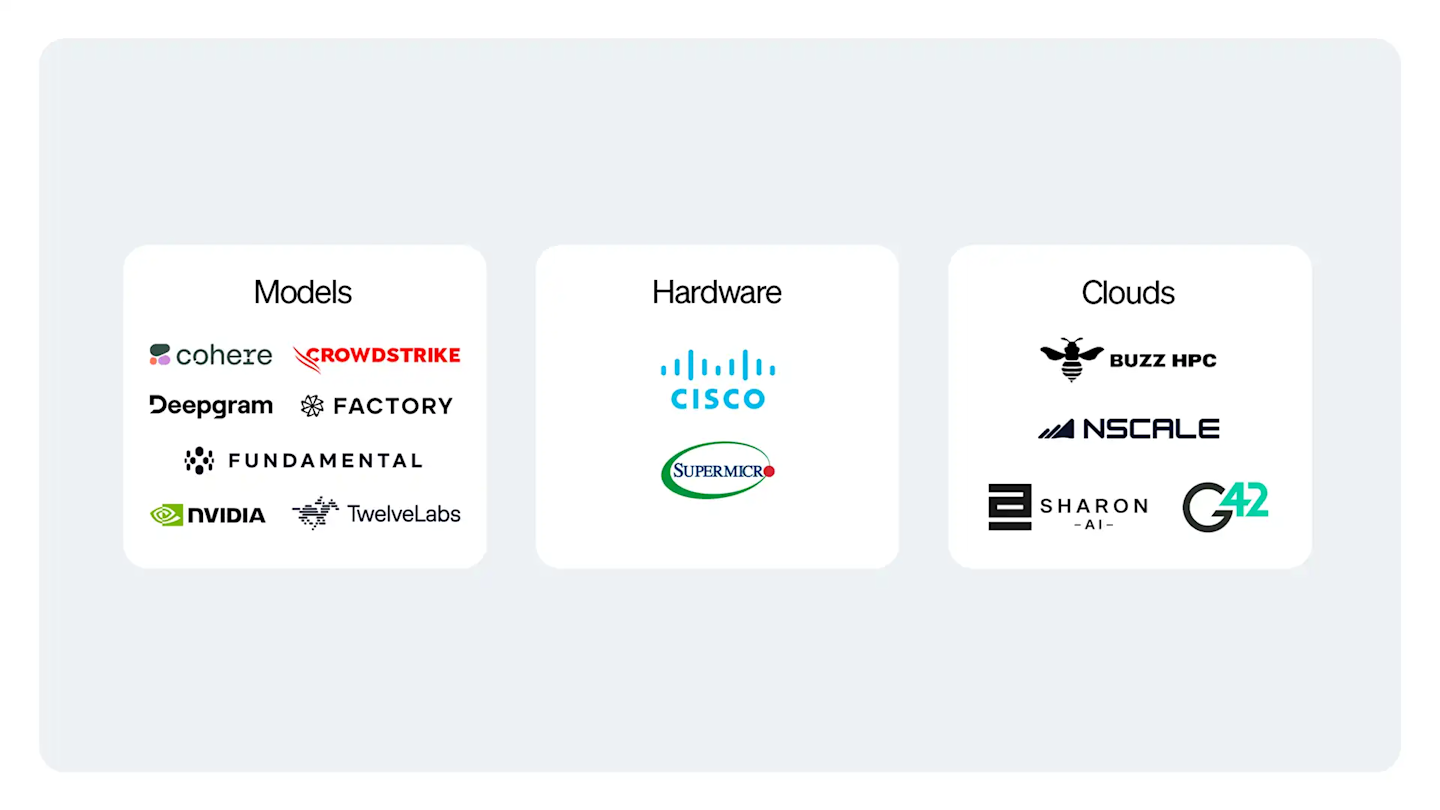
Feature Details
The Architecture Behind Confidential AI
VAST DataEnclave combines secure execution, cryptographic attestation, customer-controlled key management, and auditable governance to protect AI workloads while data is in action.
Confidential Execution
Attestation & Trust
Keys & Deployment
Secure Runtime
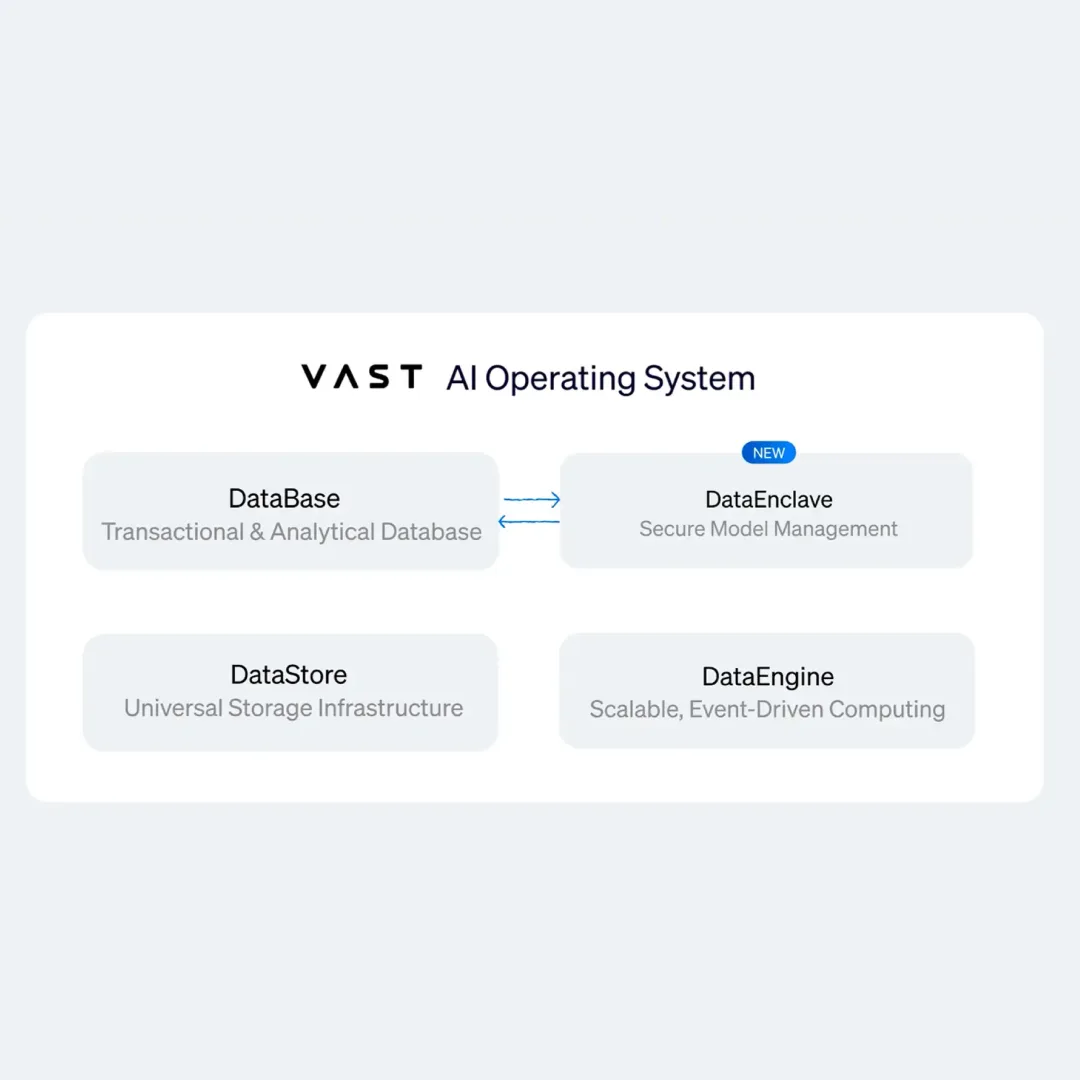
VAST DataEnclave’s secure container runtime is delivered as a capability of VAST DataEngine, providing hardware-backed isolation for containerized AI workloads while maintaining familiar application packaging and deployment.
CoCo Compatible
The VAST DataEnclave secure runtime is compatible with the CNCF Confidential Containers (CoCo) ecosystem, including runtimes such as Kata Containers, providing an open foundation for confidential container execution.
Hardware Isolation
Confidential execution protects sensitive data and model assets from privileged infrastructure administrators, creating a hardware-isolated environment for processing sensitive enterprise data with proprietary AI models.
Accelerated AI
Run AI across CPUs and GPUs operating in Confidential Computing mode, with hardware-backed protections that safeguard sensitive data and model assets from the underlying infrastructure throughout accelerated processing.
Explore the Future of Confidential Enterprise AI
Solution Brief
VAST DataEnclave Confidential AI Solution Brief
Learn how VAST DataEnclave enables advanced AI to operate securely on regulated and sensitive enterprise data.
Analyst Paper
Bringing Frontier Models to Regulated Enterprise Data
Learn how VAST DataEnclave brings proprietary AI models to sensitive enterprise data with hardware-isolated execution, cryptographic attestation, and independent control of protected assets.
White Paper
VAST DataEnclave Architecture and Trust Model
This technical white paper examines the VAST DataEnclave architecture, including hardware-isolated execution, cryptographic attestation, key management, confidential GPU acceleration, and auditability. Learn how verify-before-decrypt protects sensitive data and proprietary AI models during processing.
FAQ
Get the Facts About VAST DataEnclave
Read the FAQConfidential AI applies confidential computing to AI workloads to protect sensitive data and model assets while they are actively being processed. VAST DataEnclave combines hardware-isolated execution, cryptographic attestation, and customer-controlled key management so protected assets become accessible only inside verified confidential environments.
VAST DataEnclave runs AI workloads inside hardware-isolated confidential environments that prevent the underlying infrastructure and its administrators from inspecting protected workload memory. Cryptographic attestation verifies the environment before the keys or secrets required to access sensitive data and models are released.
Before protected data or models can be accessed, VAST DataEnclave cryptographically verifies that the hardware, software environment, and workload configuration meet approved security requirements. If verification fails, the necessary keys and secrets remain unavailable, preventing the protected assets from being decrypted inside an untrusted environment.
The owners of protected assets retain control of their keys. Enterprise data can remain protected by customer-controlled keys while proprietary model weights remain under the model provider’s control. VAST DataEnclave integrates with existing key management infrastructure, including AWS KMS, Google Cloud KMS, Microsoft Azure Key Vault, HashiCorp Vault, Thales, and Fortanix, rather than requiring VAST to own the keys.
Yes. VAST DataEnclave creates a neutral, verified environment where proprietary models can operate against sensitive enterprise data while both remain protected. This enables enterprises to use advanced proprietary models without surrendering control of their data, while model providers can securely serve those customers without exposing their model IP.
Yes. VAST DataEnclave is designed for both connected and fully air-gapped deployments. Connected environments use VAST-managed attestation built on open confidential computing technologies, while fully air-gapped environments support on-premises attestation and key brokering without requiring external network connectivity.
No. VAST DataEnclave is the confidential AI capability of VAST DataEngine, combining secure container execution and cryptographic attestation with customer-controlled and third-party key management infrastructure. It extends the VAST AI Operating System with confidential execution for sensitive AI workloads without introducing another engine or infrastructure layer.
VAST DataEnclave maintains a tamper-proof, queryable audit trail of attestation events, key releases, policy decisions, and workload lifecycle activity. Security and compliance teams can verify what ran, where, and under what approved policy without exposing the sensitive data or proprietary models protected inside the confidential environment.
Bring AI to Sensitive Data
Unlock AI initiatives that security, sovereignty, and regulatory requirements once put out of reach with verified confidential execution from VAST.