The 5 Pillars of Private Cloud Storage for Kubernetes
Kubernetes has become the control plane for modern infrastructure. But if data remains trapped in legacy silos - file in one system, object in another, block somewhere else - operations stop being cloud‑like. To truly deliver cloud-native agility across both compute and data, enterprises need a platform that unifies access, simplifies multitenancy, automates operations, and scales without friction.
VAST Data brings all application types, protocols, and performance tiers into a single globally efficient data layer that fits naturally into the Kubernetes operating model. And we’ve identified five pillars, derived from years of working with the most demanding private‑cloud deployments, that ensure organizations get the most from Kubernetes while delivering a true cloud‑like storage experience.
Pillar 1: CSP‑Grade Multitenancy
Multitenancy is essential in any environment offering cloud‑like access to internal or external teams. Kubernetes already handles compute and networking segmentation well through namespaces and policies, and VAST extends this to the data domain.
The VAST AI OS enables each tenant to operate as an isolated storage domain with unique credentials, quotas, directory structures, S3 access keys, and security policies. Virtual IP pools, client filtering, and per‑tenant DNS services allow complete separation of traffic and administration.
Because tenants map cleanly to Kubernetes namespaces and StorageClasses, organizations can safely onboard teams knowing that data access, security, and consumption policies remain isolated, while still benefiting from shared global efficiency.
Pillar 2: A Unified Data Layer for File, Block, and Object
Kubernetes was built to give developers infrastructure abstraction and freedom. But that flexibility breaks down if storage only supports some of the access patterns that applications require.
VAST natively supports:
- NFS for POSIX‑based microservices
- Block storage for stateful applications and databases
- S3‑compatible object storage for modern analytics and AI pipelines
They’re all accessed from the same system, the same namespace, and the same control plane.
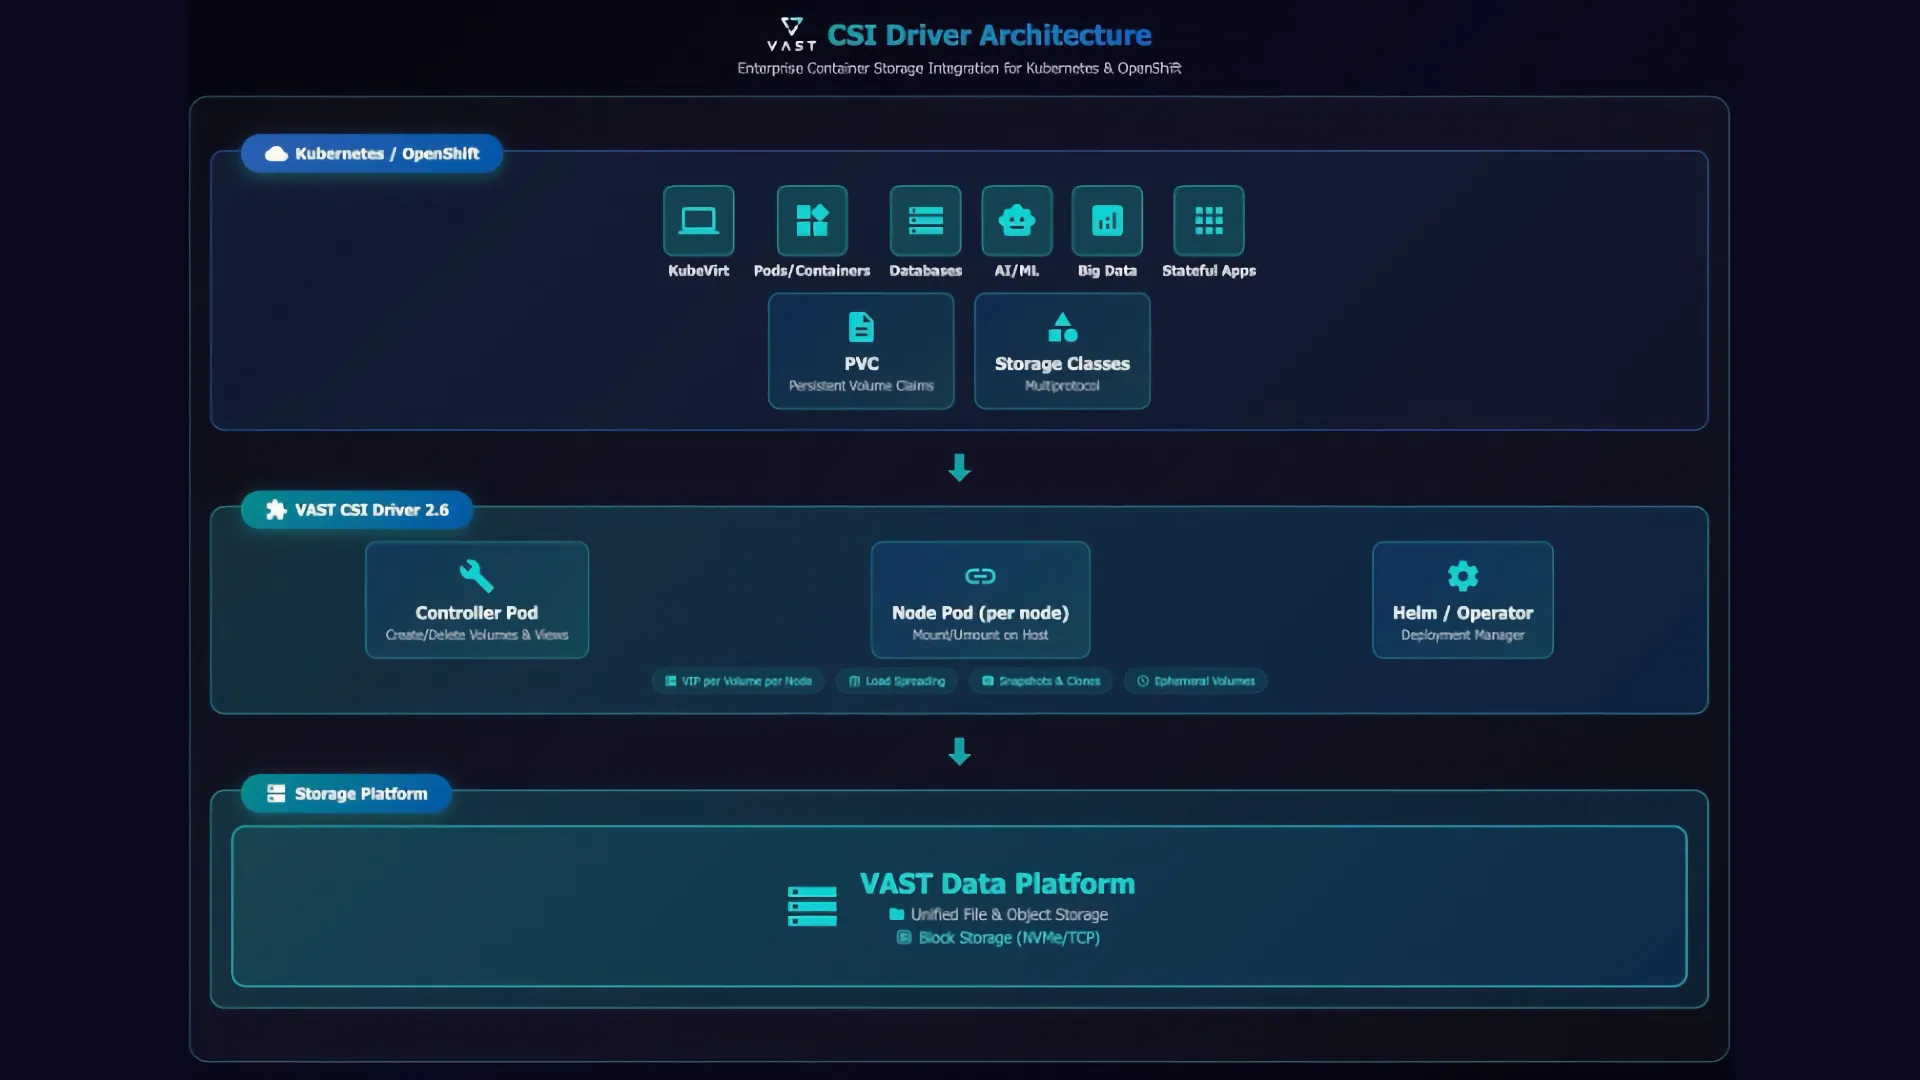
The VAST CSI driver delivers both block and file‑based persistent volumes from Kubernetes, while the COSI driver delivers bucket-based object storage. Applications can even mix protocols. For example, an AI pipeline can write files over NFS while training stacks read the same data through S3 - no copying, no indexing delays.
Where other platforms deliver only two of these three, or require separate silos to achieve them, VAST keeps everything unified and responsive.
Pillar 3: Maximum Storage Efficiency Through Consolidation
Private cloud efforts often succeed or fail based on how efficiently data is managed. Multiple isolated storage systems force elevated costs and administrative burden.
With VAST, when many workloads consolidate into one global namespace, the platform applies a combination of global deduplication, similarity reduction, and compression — inline and at scale. This takes place regardless of whether data is written as block, file, or object.
The result: the more teams and workloads that join the platform, the better the efficiency. Customers avoid costly re‑architecting or scrambling for extra capacity; they simply scale when needed.
Pillar 4: Broad VM and Container Support (Modernization on Your Terms)
Large enterprises don’t flip from legacy infrastructure to containers overnight. Many still run significant portions of their business on VMs.
VAST supports modernization at any pace:
- Kubernetes container workloads via CSI/COSI
- KubeVirt VMs, using the same persistent volume workflows
- VMware, Hyper‑V, OpenStack, and existing platforms remain fully supported
A VM running on KubeVirt today and a containerized service tomorrow are both backed by the same volumes and storage policies. No data migrations, no application downtime, no operational retraining.
Pillar 5: Minimal Operational Complexity with API‑First Automation
Cloud‑native success depends on automation and GitOps‑style operations. VAST was designed from day one to make every capability - provisioning, snapshots, tenants, security - fully programmable. This API‑first approach means Kubernetes operators can define and manage storage declaratively, using the same pipelines and tooling they use to manage compute.
Meanwhile, VAST’s scale‑out architecture expands performance and capacity non-disruptively. There is no rebalancing, no forklift upgrades, and no additional performance tuning required. Storage simply stays out of the way while the organization focuses on application value.
A Data Platform That Scales with Your Kubernetes Vision
Whether modernizing your infrastructure, deploying AI workloads, or building your own cloud services, VAST lets teams evolve on their schedule, without rewriting data access patterns or ever migrating data between systems.
With VAST, storage looks like cloud: Flexible. Automated. Efficient. Programmable.
Come meet the VAST team at KubeCon (Booth #1741) to see how we’re helping organizations deliver cloud-like storage experiences for Kubernetes without complexity.